Federated Apps
Federated Applications in Descope enable you to establish secure Single Sign-On (SSO) connections between your applications and Descope's authentication system. This allows users to authenticate once with Descope and gain access to multiple connected applications without needing to log in separately to each one.
Descope supports two main types of federated applications:
When connecting to an application using either OIDC or SAML, Descope acts as the Federated Identity Provider (IdP), allowing you to unify your users' login experience across multiple applications.
You can configure and manage these federated applications through the Federated Apps tab in the Descope Console, or through our Management SDKs.
Note
Configuring federated applications is a Pro/Enterprise-tier feature.
Associating Users with Applications
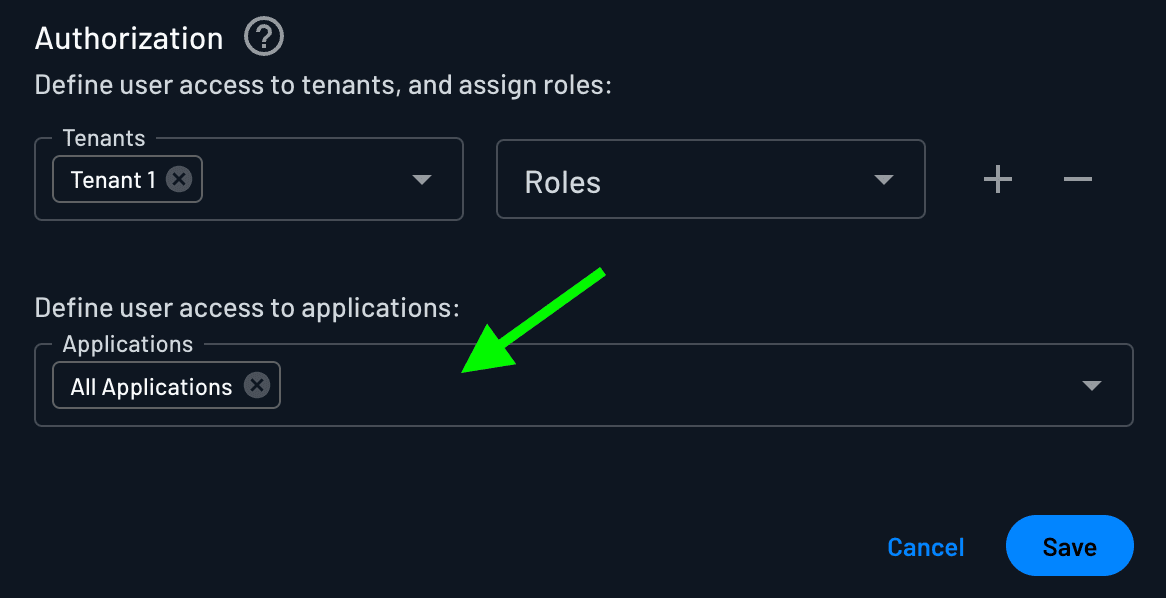
Descope allows you to control which users can access specific federated applications either through the console (as pictured below), or with our management SDKs.
Additionally, federated applications can be automatically assigned to users based on their tenant assignment.
How Descope Checks App Access
Descope decides access from the list of apps assigned to the user, not from a setting on each app. A federated app has no "allow all users" option. Every app checks the same user list in the same way:
- A user with no assigned apps: The user can sign in to every federated app in the project.
- A user with at least one assigned app: The user can sign in only to the apps on their own list, or to apps assigned to one of their tenants through Application Access. Every other federated app refuses the user.
- A session with a current tenant: Descope counts only the apps assigned to that tenant, together with the apps assigned to the user directly. Apps assigned to the user's other tenants don't count.
Because of this rule, the first assignment changes what a user can reach. A user who could sign in to every app before can sign in only to the assigned app afterward. If you assign a user to one app, you would also assign them to every other federated app they still need, or assign those apps to their tenant.
When Descope refuses a user, the sign-in fails with the error E062023. See SSO error codes.
You can also change the default for users with no assigned apps. In the Console, go to Project Settings, and under Federated Apps, set Default access for new users to Do not give access to any applications. With that setting, a user with no assigned apps can't sign in to any federated app until you assign one. The default is Give access to all applications. The label says new users, but Descope applies the setting to every user who has no assigned apps when they sign in.