Descope Management
The Descope service enables granular configuration and management of their Descope instance. Within the Descope UI, you will see the manage section on the left-hand side. This area within the UI allows you to manage your users, access keys, tenants, and authorization and also contains your project's audit trail.
You can learn more about the various customizations and management under the following articles.
Management Keys
Note
You can create keys on the management keys page in the Console.
Use a management key with your Project ID to call the management SDK or API.
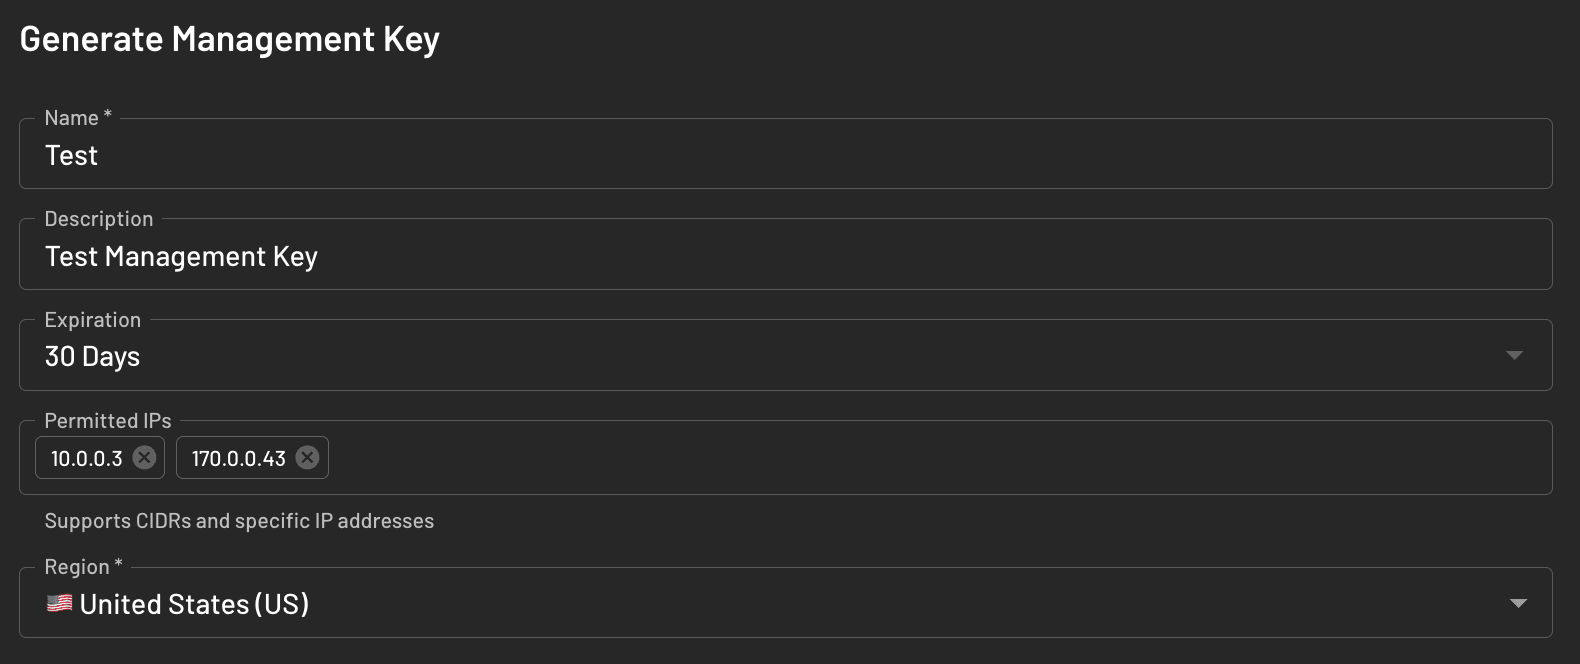
When you create a key, you set a name and an expiration (30, 60, or 90 days, or never). You can also bind it to specific projects in your company. That association is set at creation and cannot be changed later.
Once you've created a key, Descope will show the key in cleartext once, so store it somewhere safe as you will not be able to view it again.
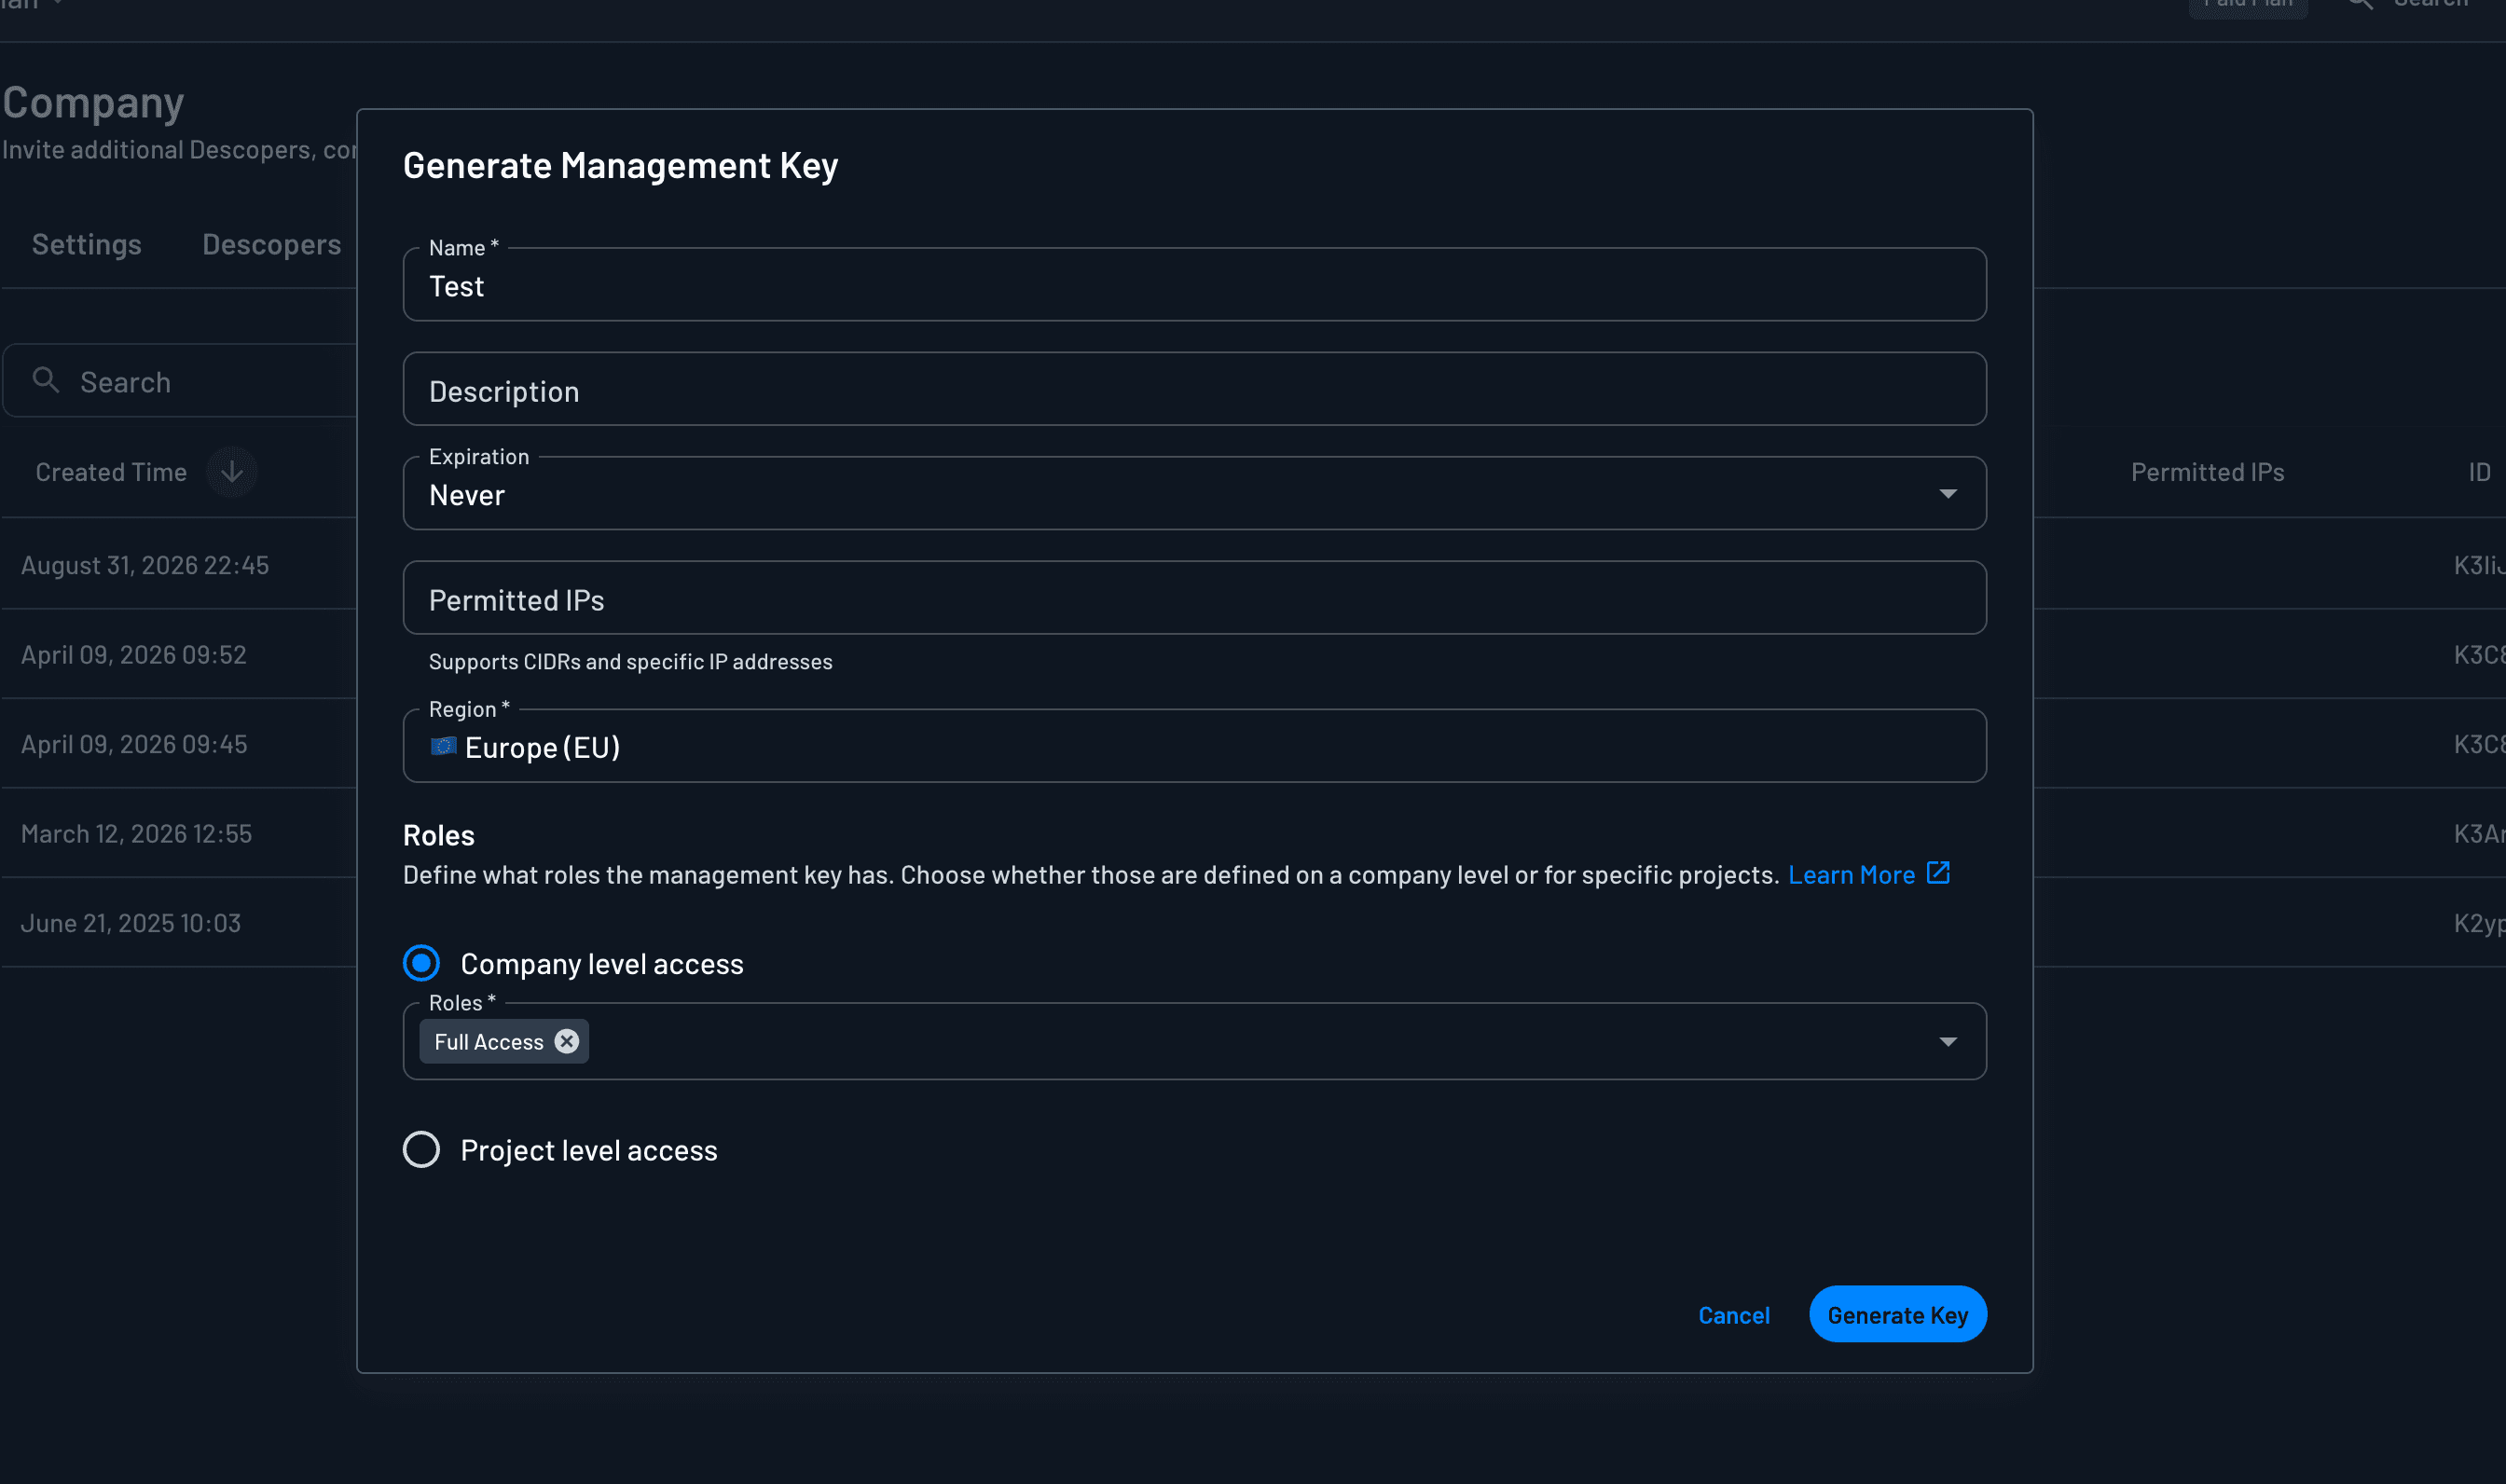
The three-dot menu on an active key offers Edit, Rotate, Deactivate, and Delete, the same actions as access keys.
Management Key Lifecycle
A management key works until it expires or is deactivated. Deactivating a key (revoking it) stops it from being used, but the key stays in the project and can be reactivated later. Deleting a key removes it from the project entirely.
Rotation is similar to revoke, in a sense that it replaces the secret while keeping the key's name, expiration, and role and project associations. The previous secret stops working immediately, and any SDK or API client still using it will fail until it has the new value.
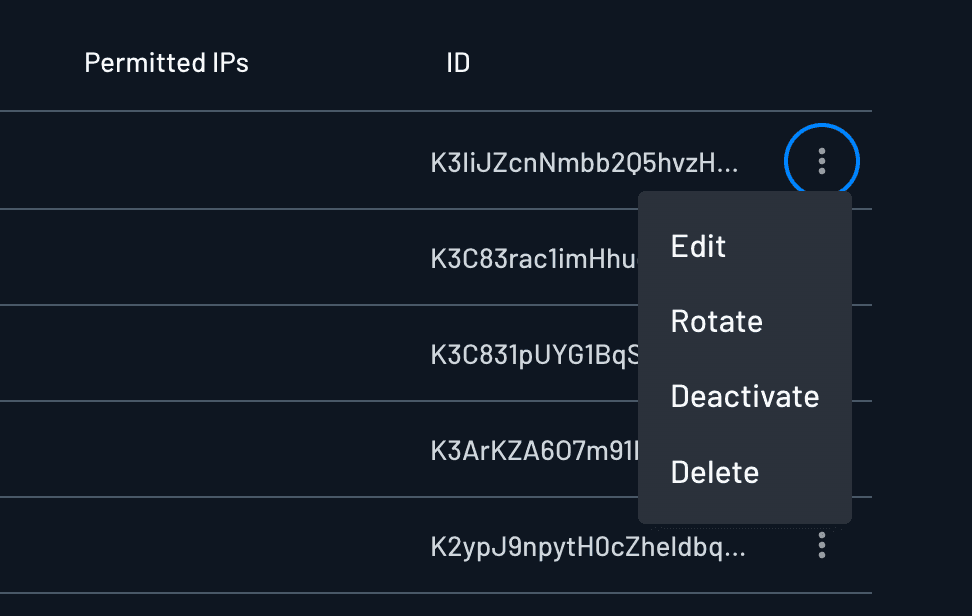
Adding Permitted IPs to Management Keys
Each management key can include a list of permitted IPs. When that list is set, the key only works from those originating addresses.
When setting permitted IPs, both CIDR ranges and individual IP addresses are supported, and the restriction applies only to that key.
Management Key Roles
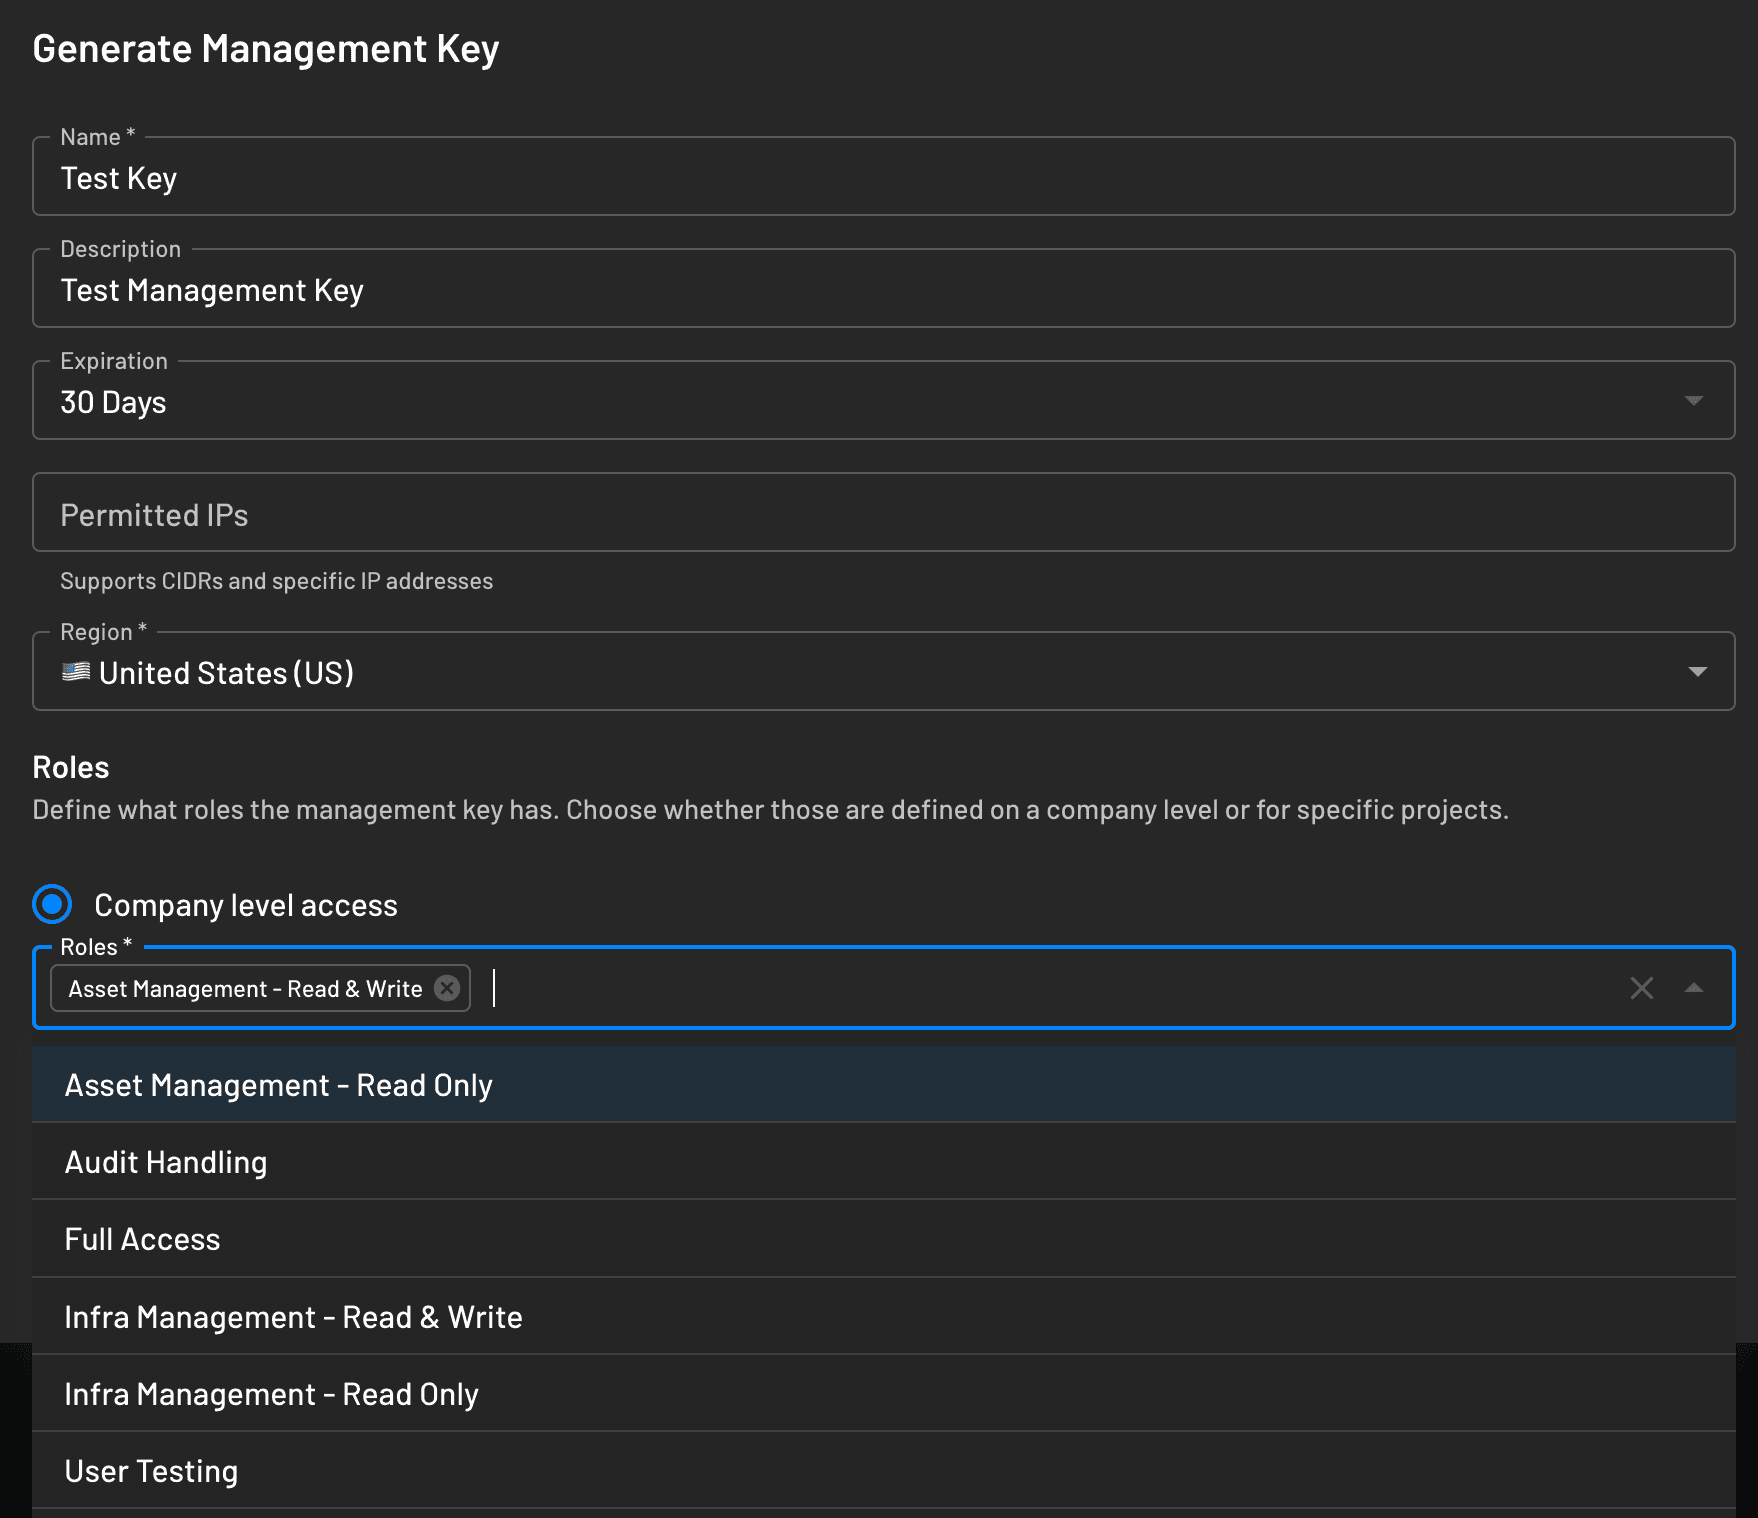
This section defines what roles the management key has. You can choose whether these roles are defined on a company level, for specific projects or for Descopers for SCIM only usage.
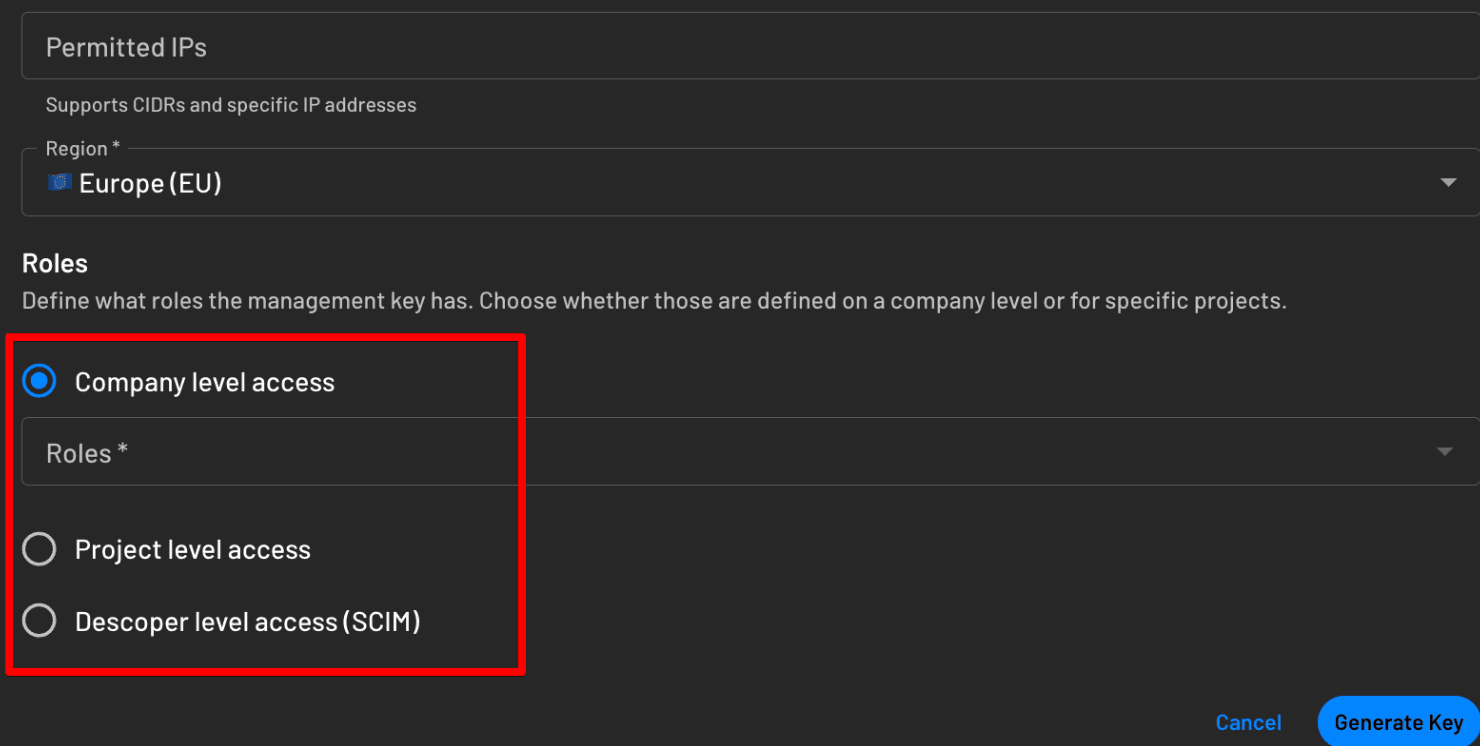
The roles available for Company level access are listed as follows:
| Roles | Machine Name | Description |
|---|---|---|
| Full Access | company-full-access | Full read and write access to all projects in region |
| User Testing | company-user-testing | Read and write access to testing APIs only |
| Asset Management - Read Only | company-asset-mgmt-read | Read access to Users, Access Keys and Tenants in all projects in region |
| Asset Management - Read & Write | company-asset-mgmt-read-write | Full read and write access to Users, Access Keys and Tenants in all projects in region |
| Audit Handling | company-audit | Read and write access to audit related APIs |
| Authentication | company-authentication | Full access to authentication methods related APIs |
| FGA - Read Only | company-fga-read | Read access to FGA/Authz related APIs |
| FGA - Read & Write | company-fga-read-write | Full read and write access to FGA/Authz related APIs |
| Infra Management - Read Only | company-infra-read | Read access to general project resources such as AuthZ, Project settings, in all projects in region |
| Infra Management - Read & Write | company-infra-read-write | Full read and write access to general project resources such as AuthZ, Project settings, in all projects in region |
| Management Keys - Read & Write | company-mgmt-keys-read-write | Full read and write access to management key management APIs |
| Descopers - Read & Write | company-descopers-read-write | Full read and write access to Descoper management APIs |
The roles available for Project level access are listed as follows:
| Roles | Machine Name | Description |
|---|---|---|
| Full Access | project-full-access | Full read and write access to the project |
| User Testing | project-user-testing | Read and write access to testing APIs only |
| Asset Management - Read Only | project-asset-mgmt-read | Read access to Users, Access Keys and Tenants in project |
| Asset Management - Read & Write | project-asset-mgmt-read-write | Full read and write access to Users, Access Keys and Tenants in project |
| Audit Handling | project-audit | Read and write access to audit related APIs |
| Authentication | project-authentication | Full access to authentication methods related APIs |
| FGA - Read Only | project-fga-read | Read access to FGA/Authz related APIs |
| FGA - Read & Write | project-fga-read-write | Full read and write access to FGA/Authz related APIs |
| Infra Management - Read Only | project-infra-read | Read access to general project resources such as AuthZ, Project settings, in project |
| Infra Management - Read & Write | project-infra-read-write | Full read and write access to general project resources such as AuthZ, Project settings, in project |
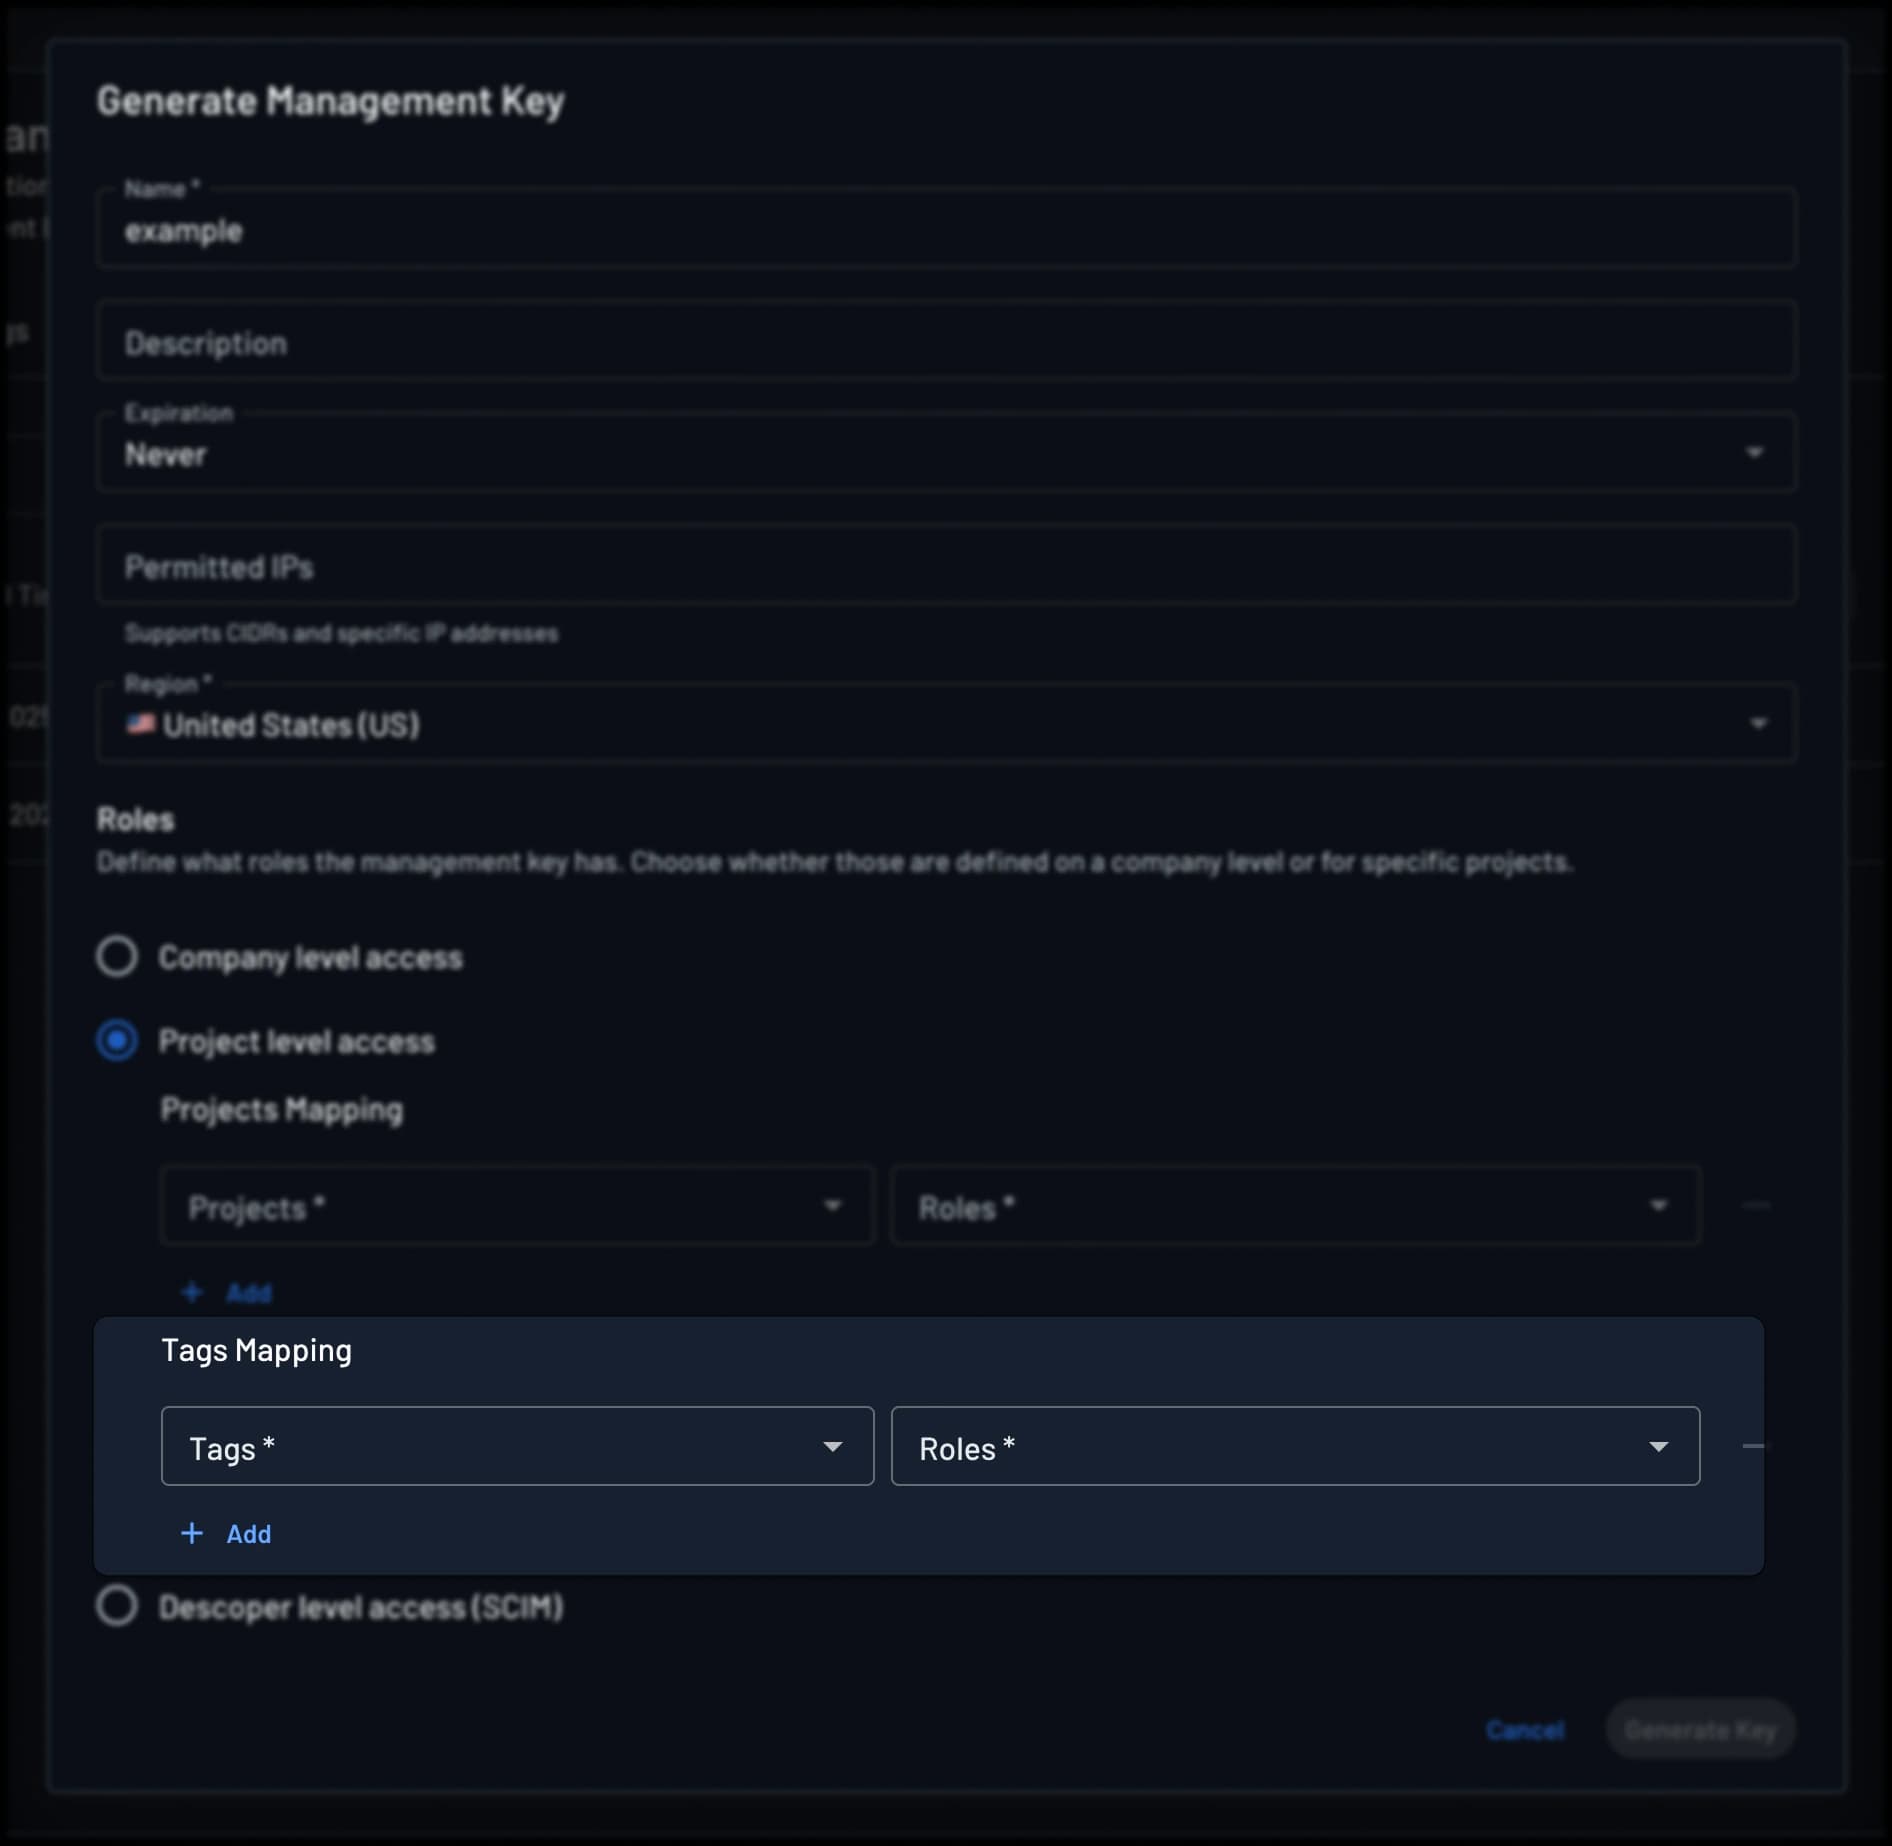
These roles for Project level access can also be applied to your project tags upon generating a management key.
Project tags, used for categorizing your projects (for example, a staging or prod tag), can be used to apply roles in your management key across all projects with the associated tag.
Note
When using roles programmatically (via API, SDK, or Terraform) for tag-level access, use the same role names as project-level but with the tag- prefix instead of project-. For example, project-full-access becomes tag-full-access, and project-asset-mgmt-read becomes tag-asset-mgmt-read.
Descoper Level access (SCIM): This level of access is when management key is used to perform SCIM related operations to control Descopers in your company.
Note
This scope is different from the above mentioned company/project level access as its referencing Descopers access level only with respect to SCIM versus referencing users on your company/project.