Company Settings
On the company page of the Descope console, you can manage company-level settings, Descopers, Descoper roles, management keys, projects, and usage. Descopers and Descoper Roles are separate tabs.
Auditing company-level changes
Actions taken on this page — such as creating or deleting projects, creating or modifying management keys, and changing company settings — are recorded as company-level audit events. To review them, see Company-level Auditing and the Company-level Audit Events reference.
Settings
Within the Settings tab, the following can be configured:
General
- The
Company Name. - The
Company ID, which is used to identity your Descope company.
Console Access
-
Enforce SSO - This will be visible once SSO is configured for the console. Will oblige Descopers to log in through SSO.
-
SSO Exclusions - This will be visible once SSO is configured for the console. Will allow you to specify login IDs that can bypass SSO authentication.
-
Force MFA - Will force Descopers to go through MFA, while allowing the Descoper to choose their preferred MFA method from the following options: Passkeys, OTP via SMS, or TOTP.
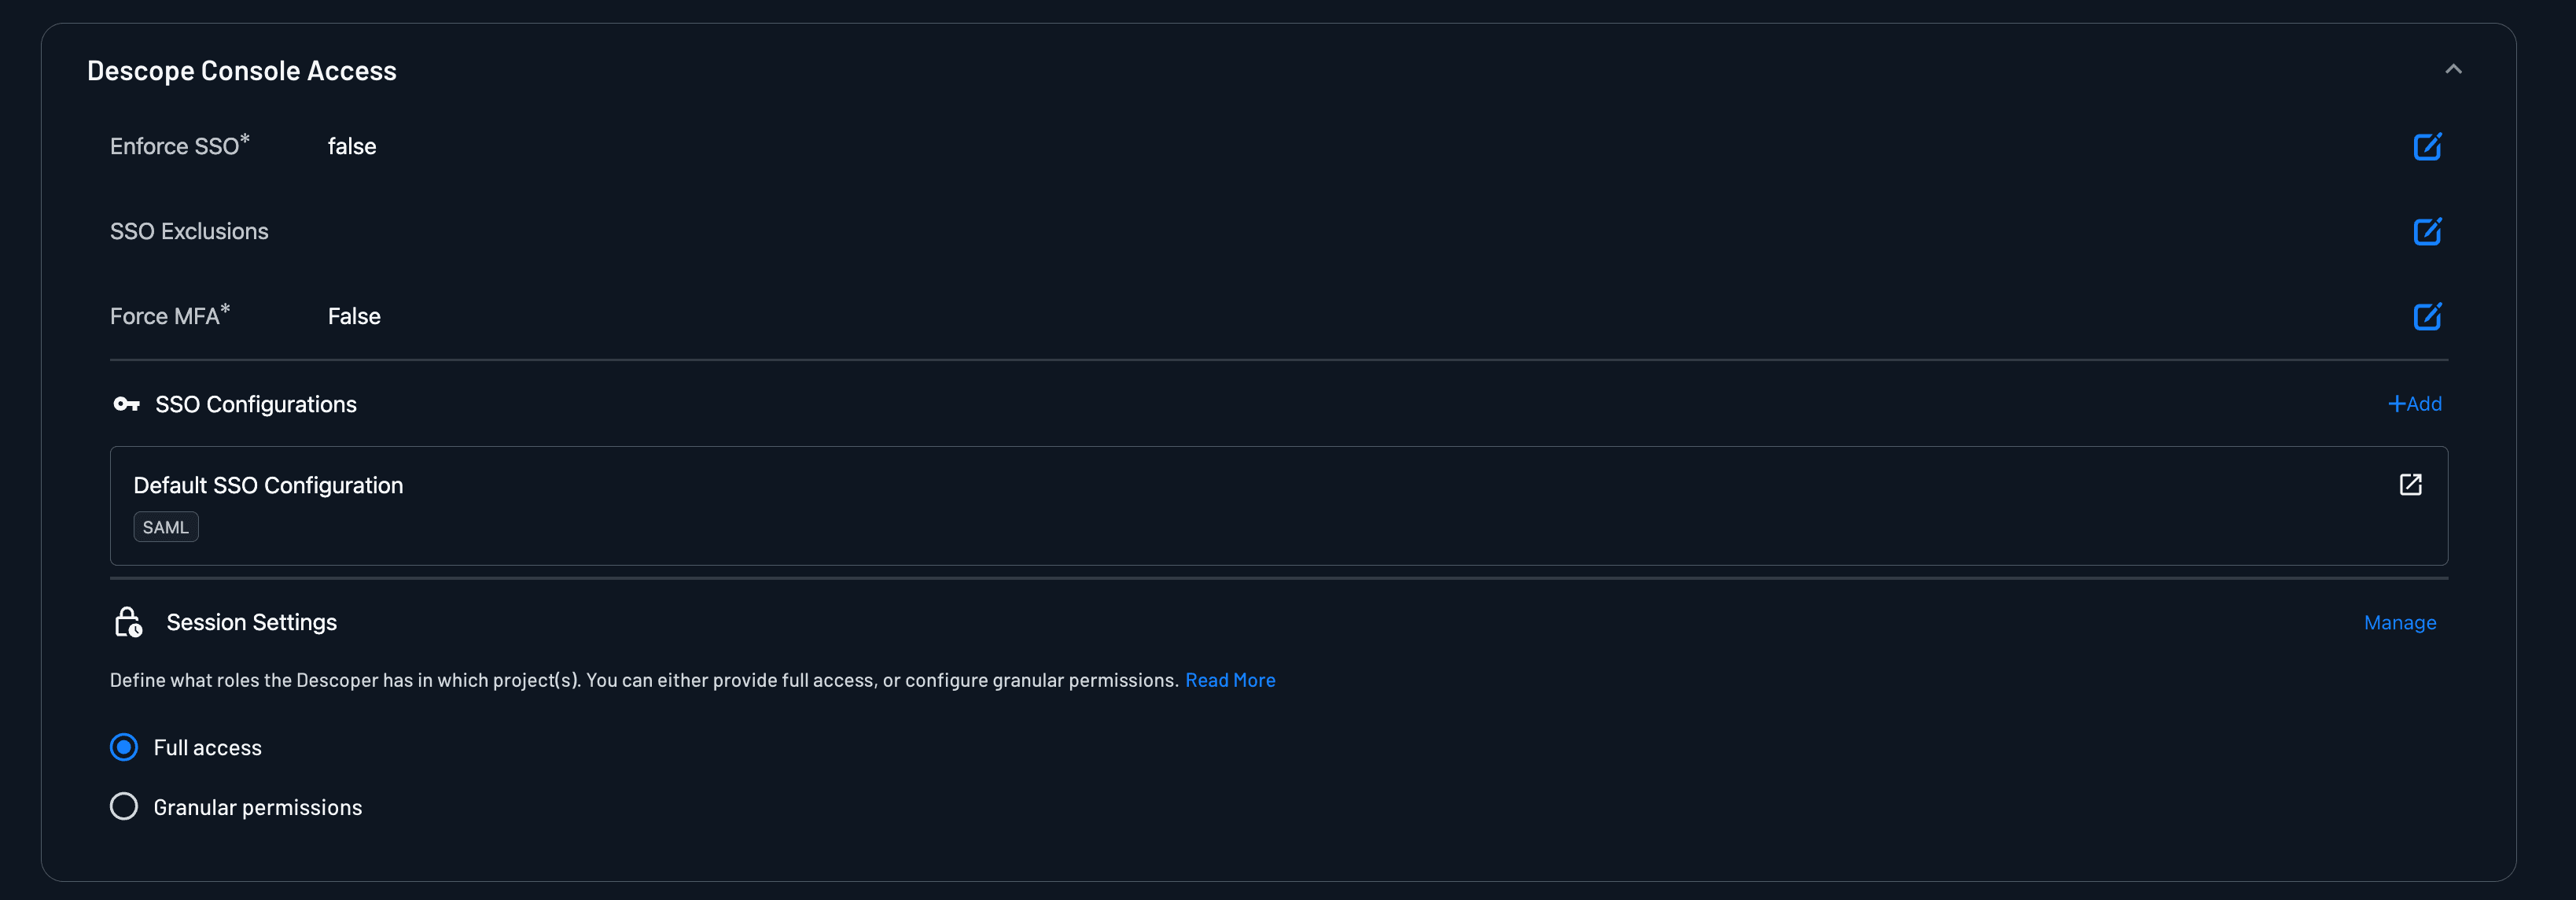
SSO Configurations
Note
Enabling Cross App Access (XAA) for your company will allow you to use XAA with the Descope MCP Server.
This section gives you your link to configure SSO for your Descope Company, using our SSO Setup Suite.
You can configure multiple SSO configurations per Company, which can be distinguished by the unique SSO domains you set in each configuration.

Within the SSO Setup Suite, you can also configure SCIM provisioning for your Descope Company. This enables you to manage Descope console access through your identity provider's SCIM provider, rather than relying on JIT (Just-In-Time) provisioning.
Group mapping for Descoper permissions is done in the Role Mapping section below.
Session Settings
You can configure session settings for your Descope Company, including session (access) token duration, session inactivity timeout, and refresh token duration.
The time units allowed for these settings are: minutes, hours, days, and weeks.
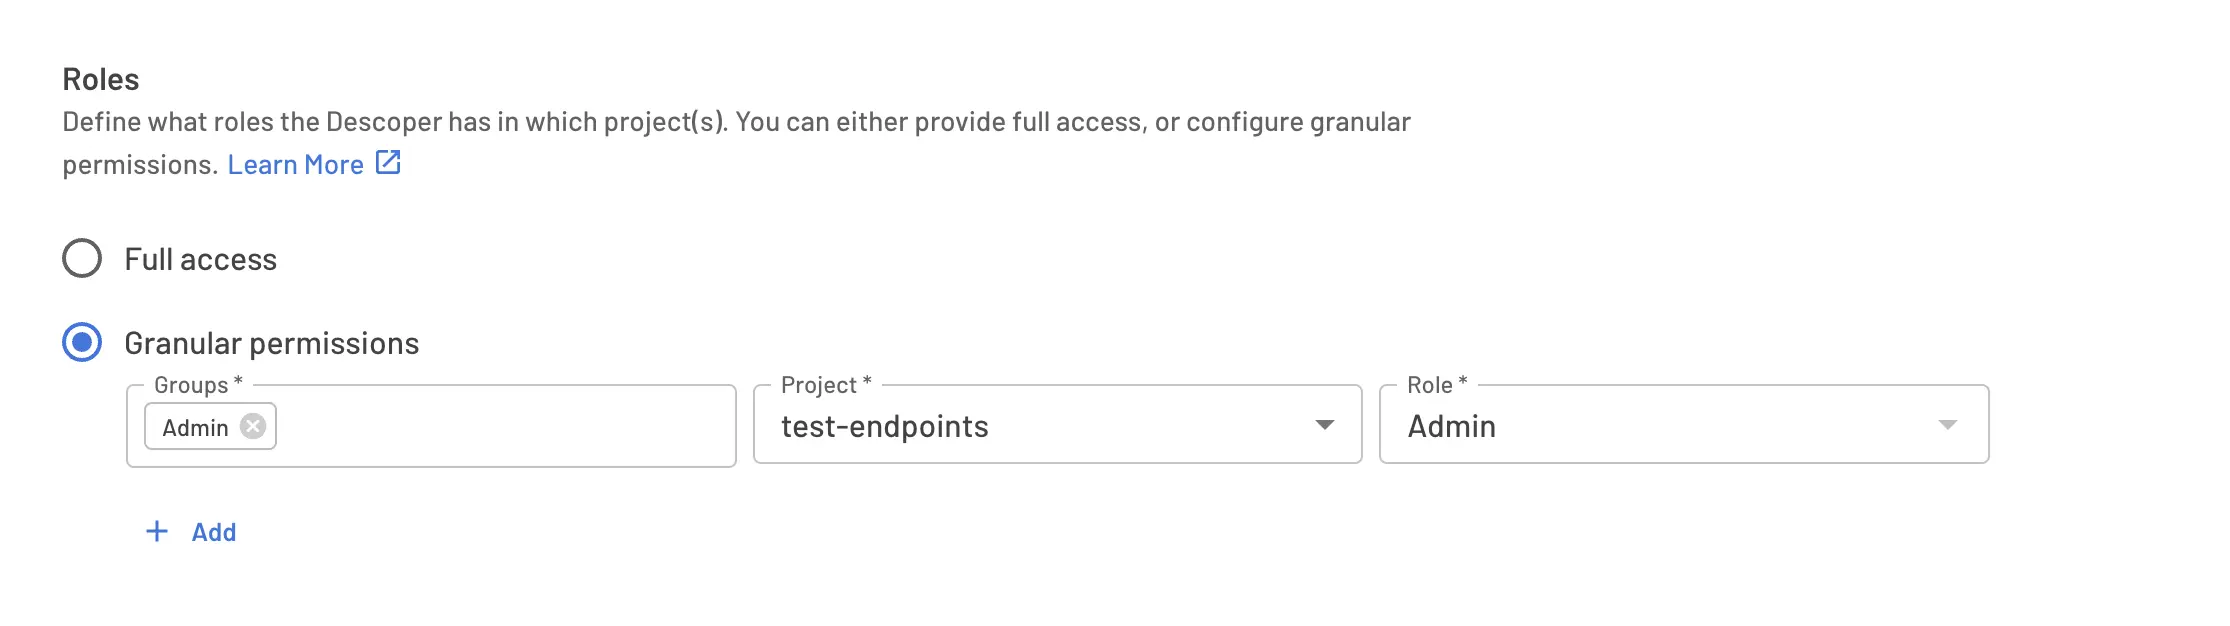
Role Mapping
At the bottom of the widget, there is a section where you can configure role mapping for your Descope Company.
You can choose to either provide full access, or configure granular permissions for users within specific groups from your SSO provider.
You can also map SSO groups to specific project-level tags, which can be associated with specific project-level roles.
Mapping SSO groups to admin access
Mapping an SSO group to Full access gives every member of that group administrative access to all projects and company settings. Mapping a group to the Admin role on specific projects gives every member full read and write access to those projects. Map only groups whose membership you control closely.
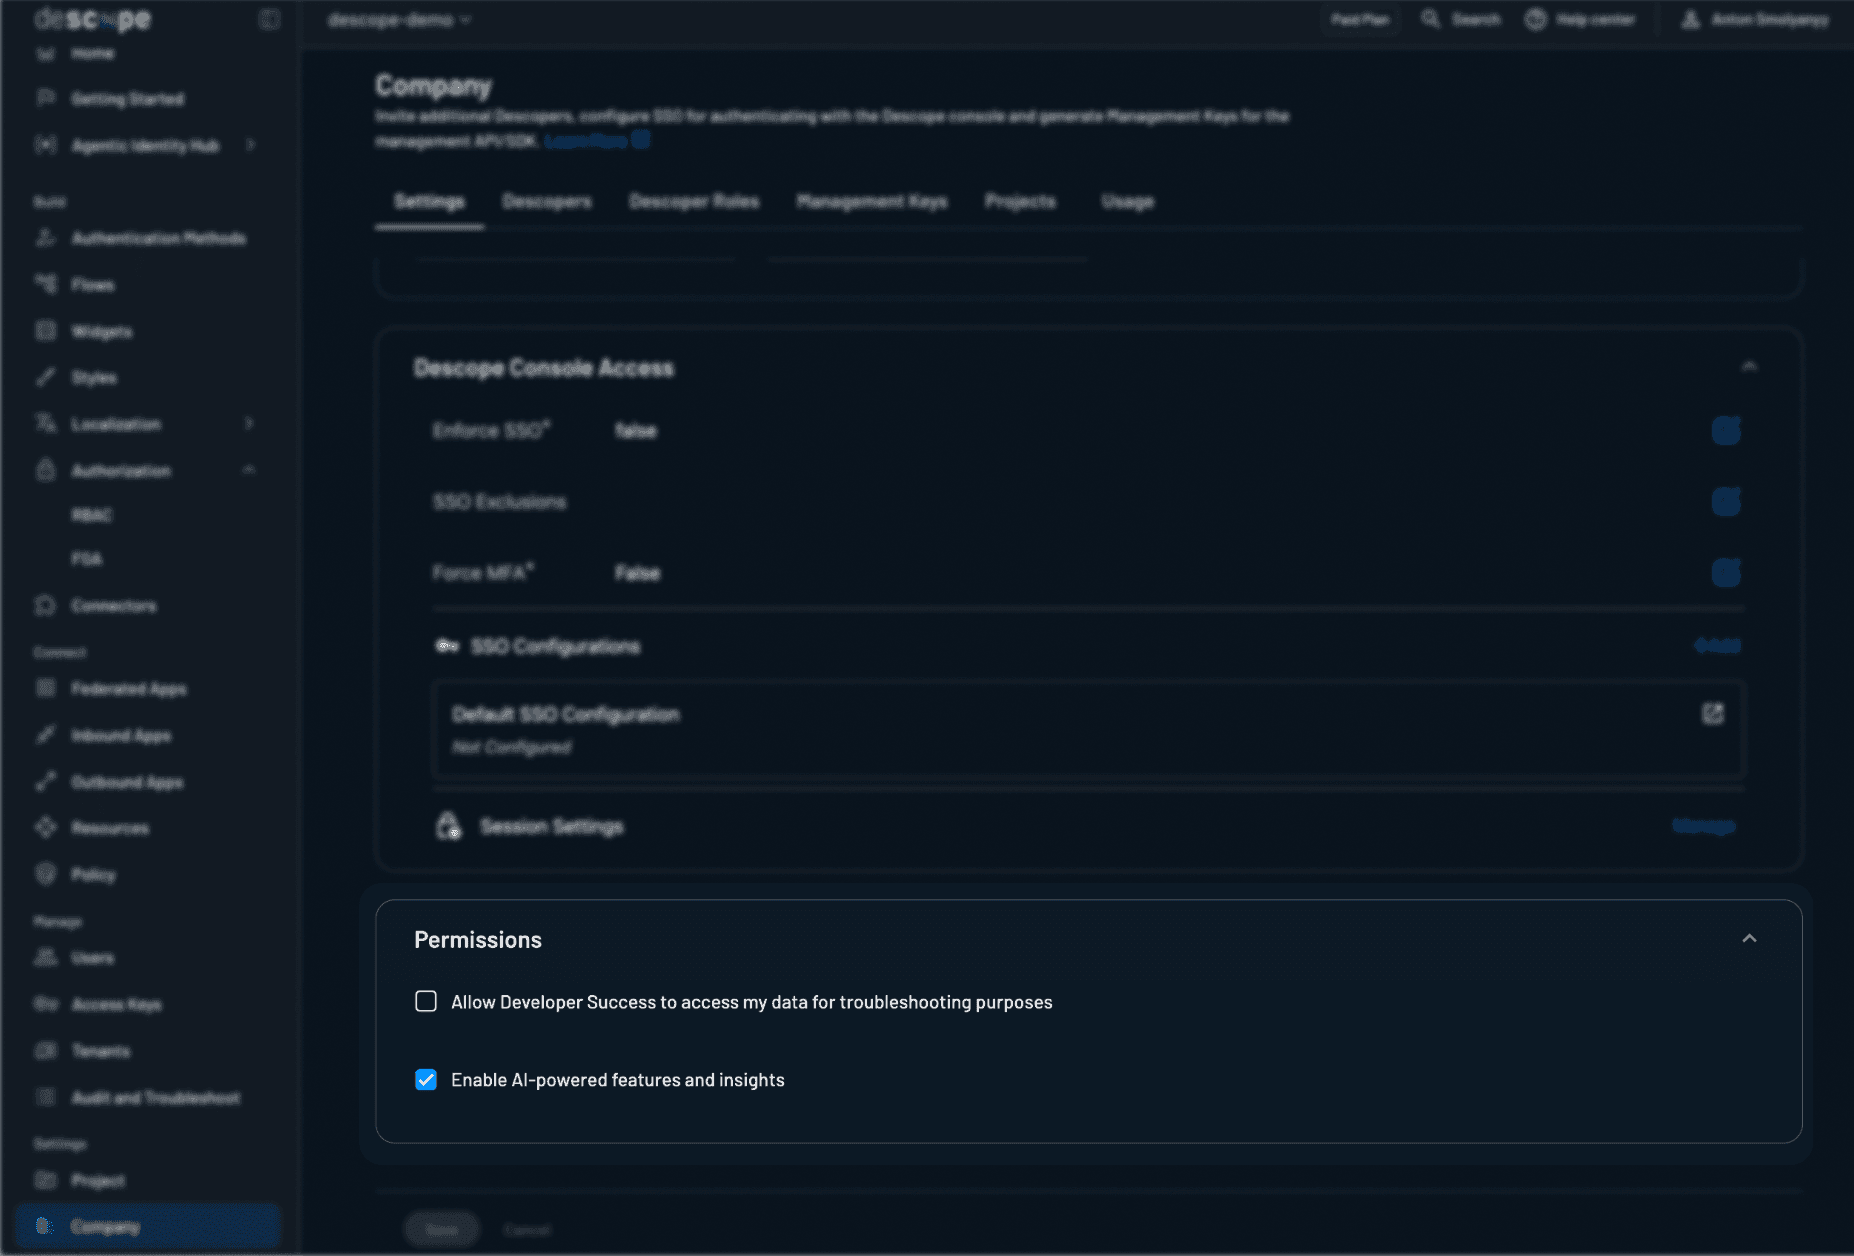
Permissions
Allow Developer Success to access my data for troubleshooting purposes: Optional. Allows the Descope Customer Success team to capture further information within the project for troubleshooting purposes.Enable AI-powered features and insights: Enables built-in AI analysis of troubleshooting logs, flow activity, flow diffs, and related data right from the Descope console. Enabled by default. Turn this toggle off if you want to disable AI features for your company to satisfy internal governance and legal requirements.
Descopers
Users who have access to your Descope Console are known as Descopers. You manage them on the Descopers tab. Roles are a separate tab. See Descoper Roles.
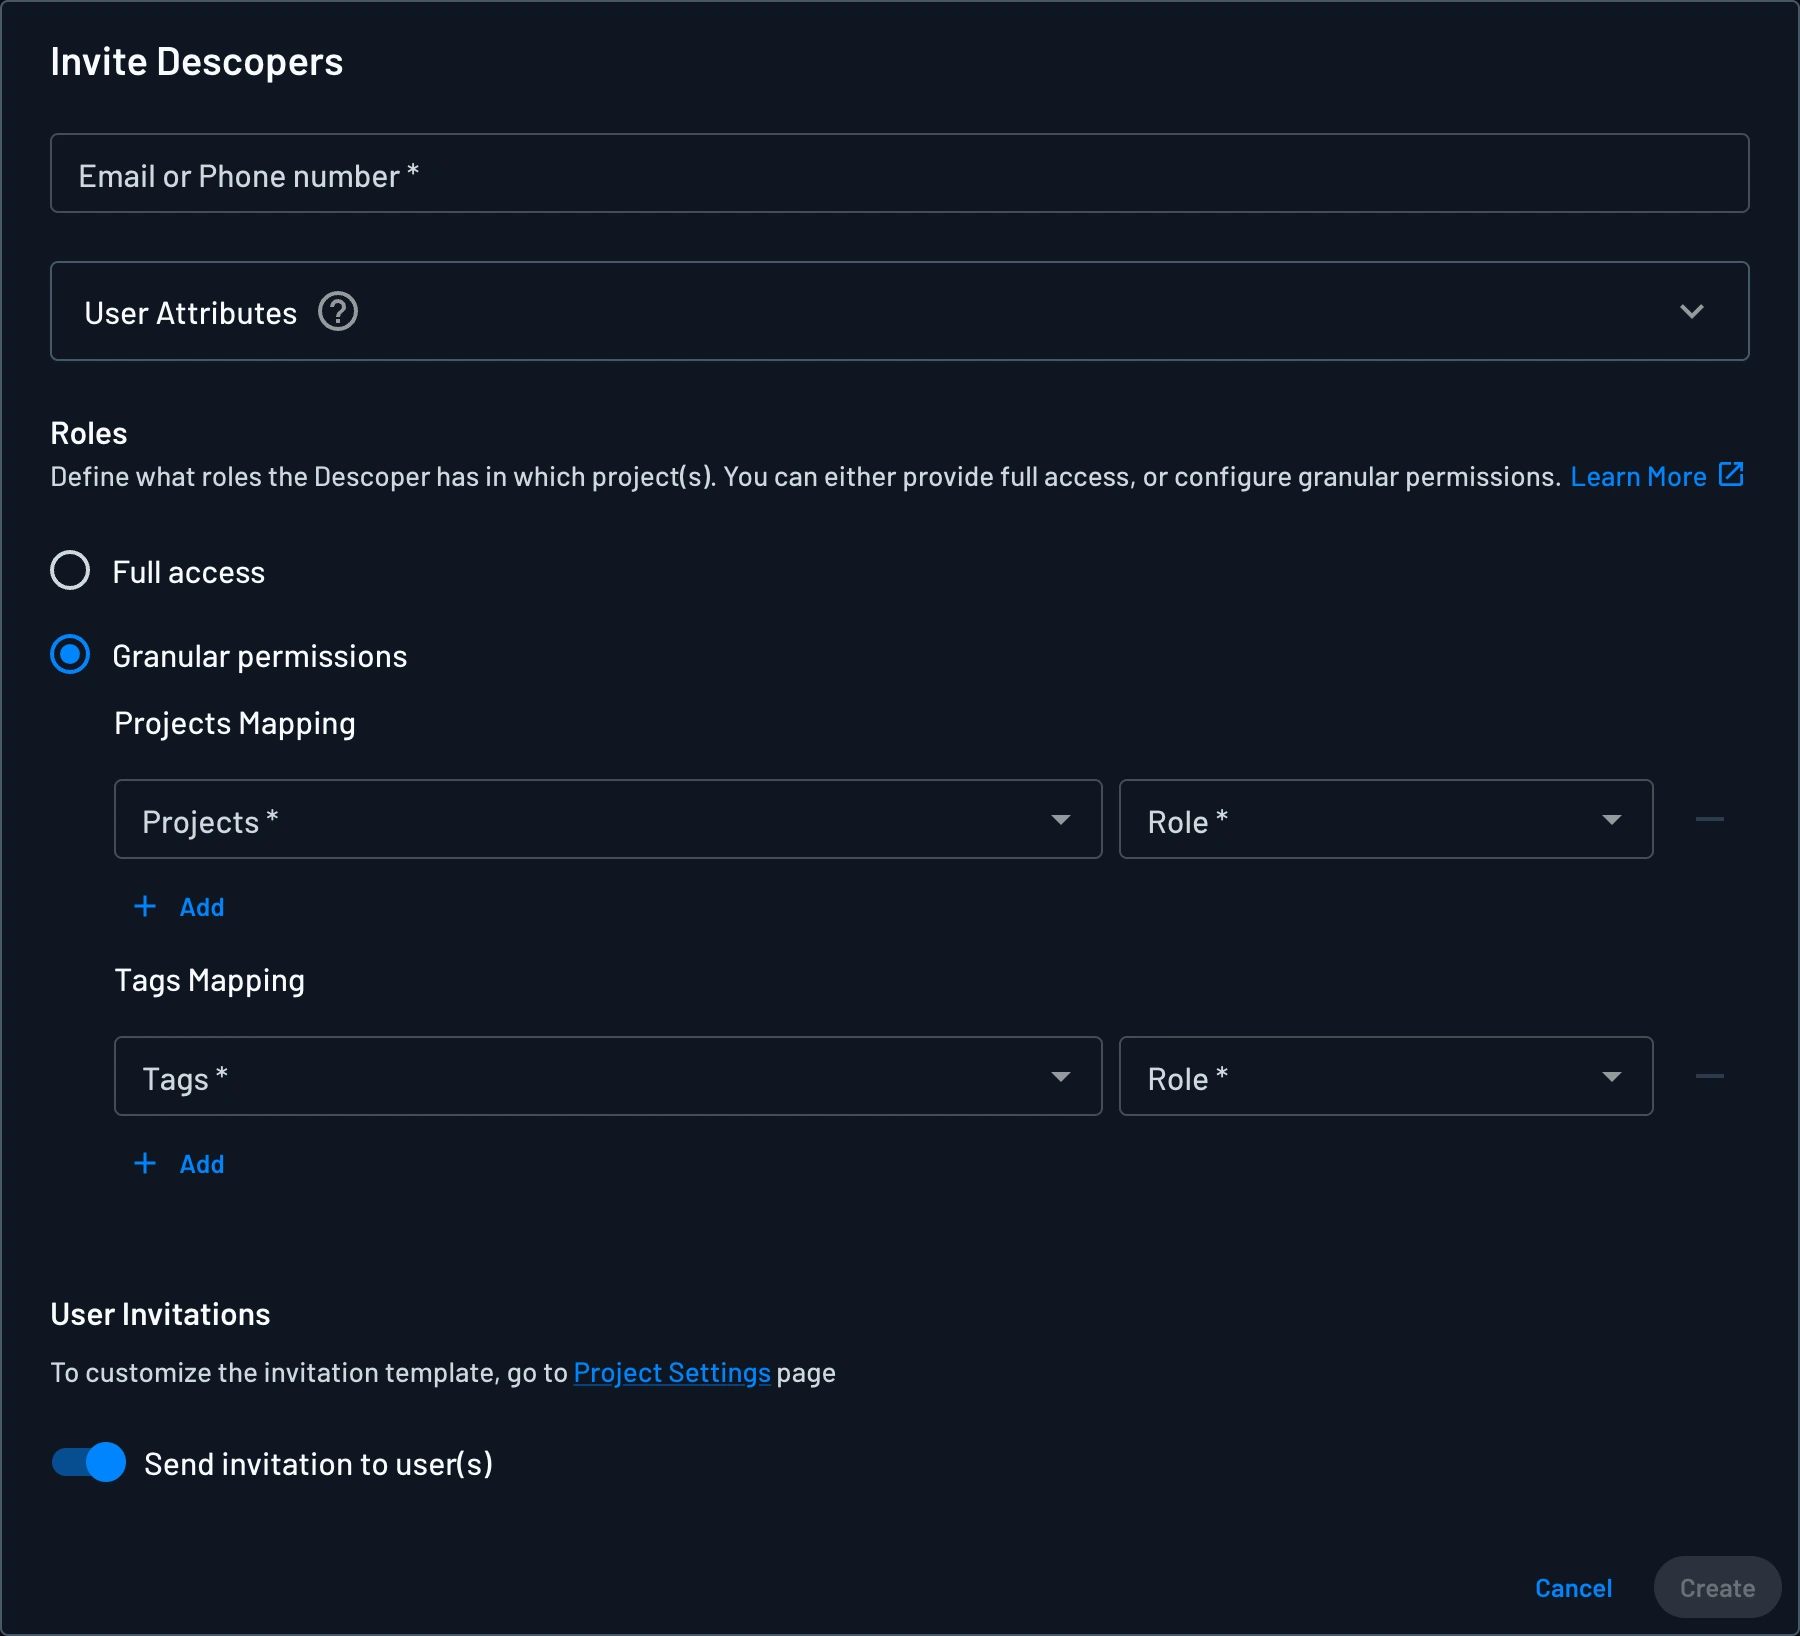
Here you can create, delete, and manage Descopers. When you create a Descoper, you can send the invitation by email and assign a role.
A Descoper can be limited to specific projects or tags. When you invite a Descoper or edit their roles, select Granular permissions instead of Full access. Under Projects Mapping, choose the projects and the role. Under Tags Mapping, choose tags and a role. A tag applies that role to every project with the tag.
Note
A Descoper can also set Sidebar Preferences to hide or show pages in their own sidebar. An administrator does not control which pages they hide.
Descoper Roles
The Descoper Roles tab lists every role, with the permission groups beside it. A role is a set of permission groups.
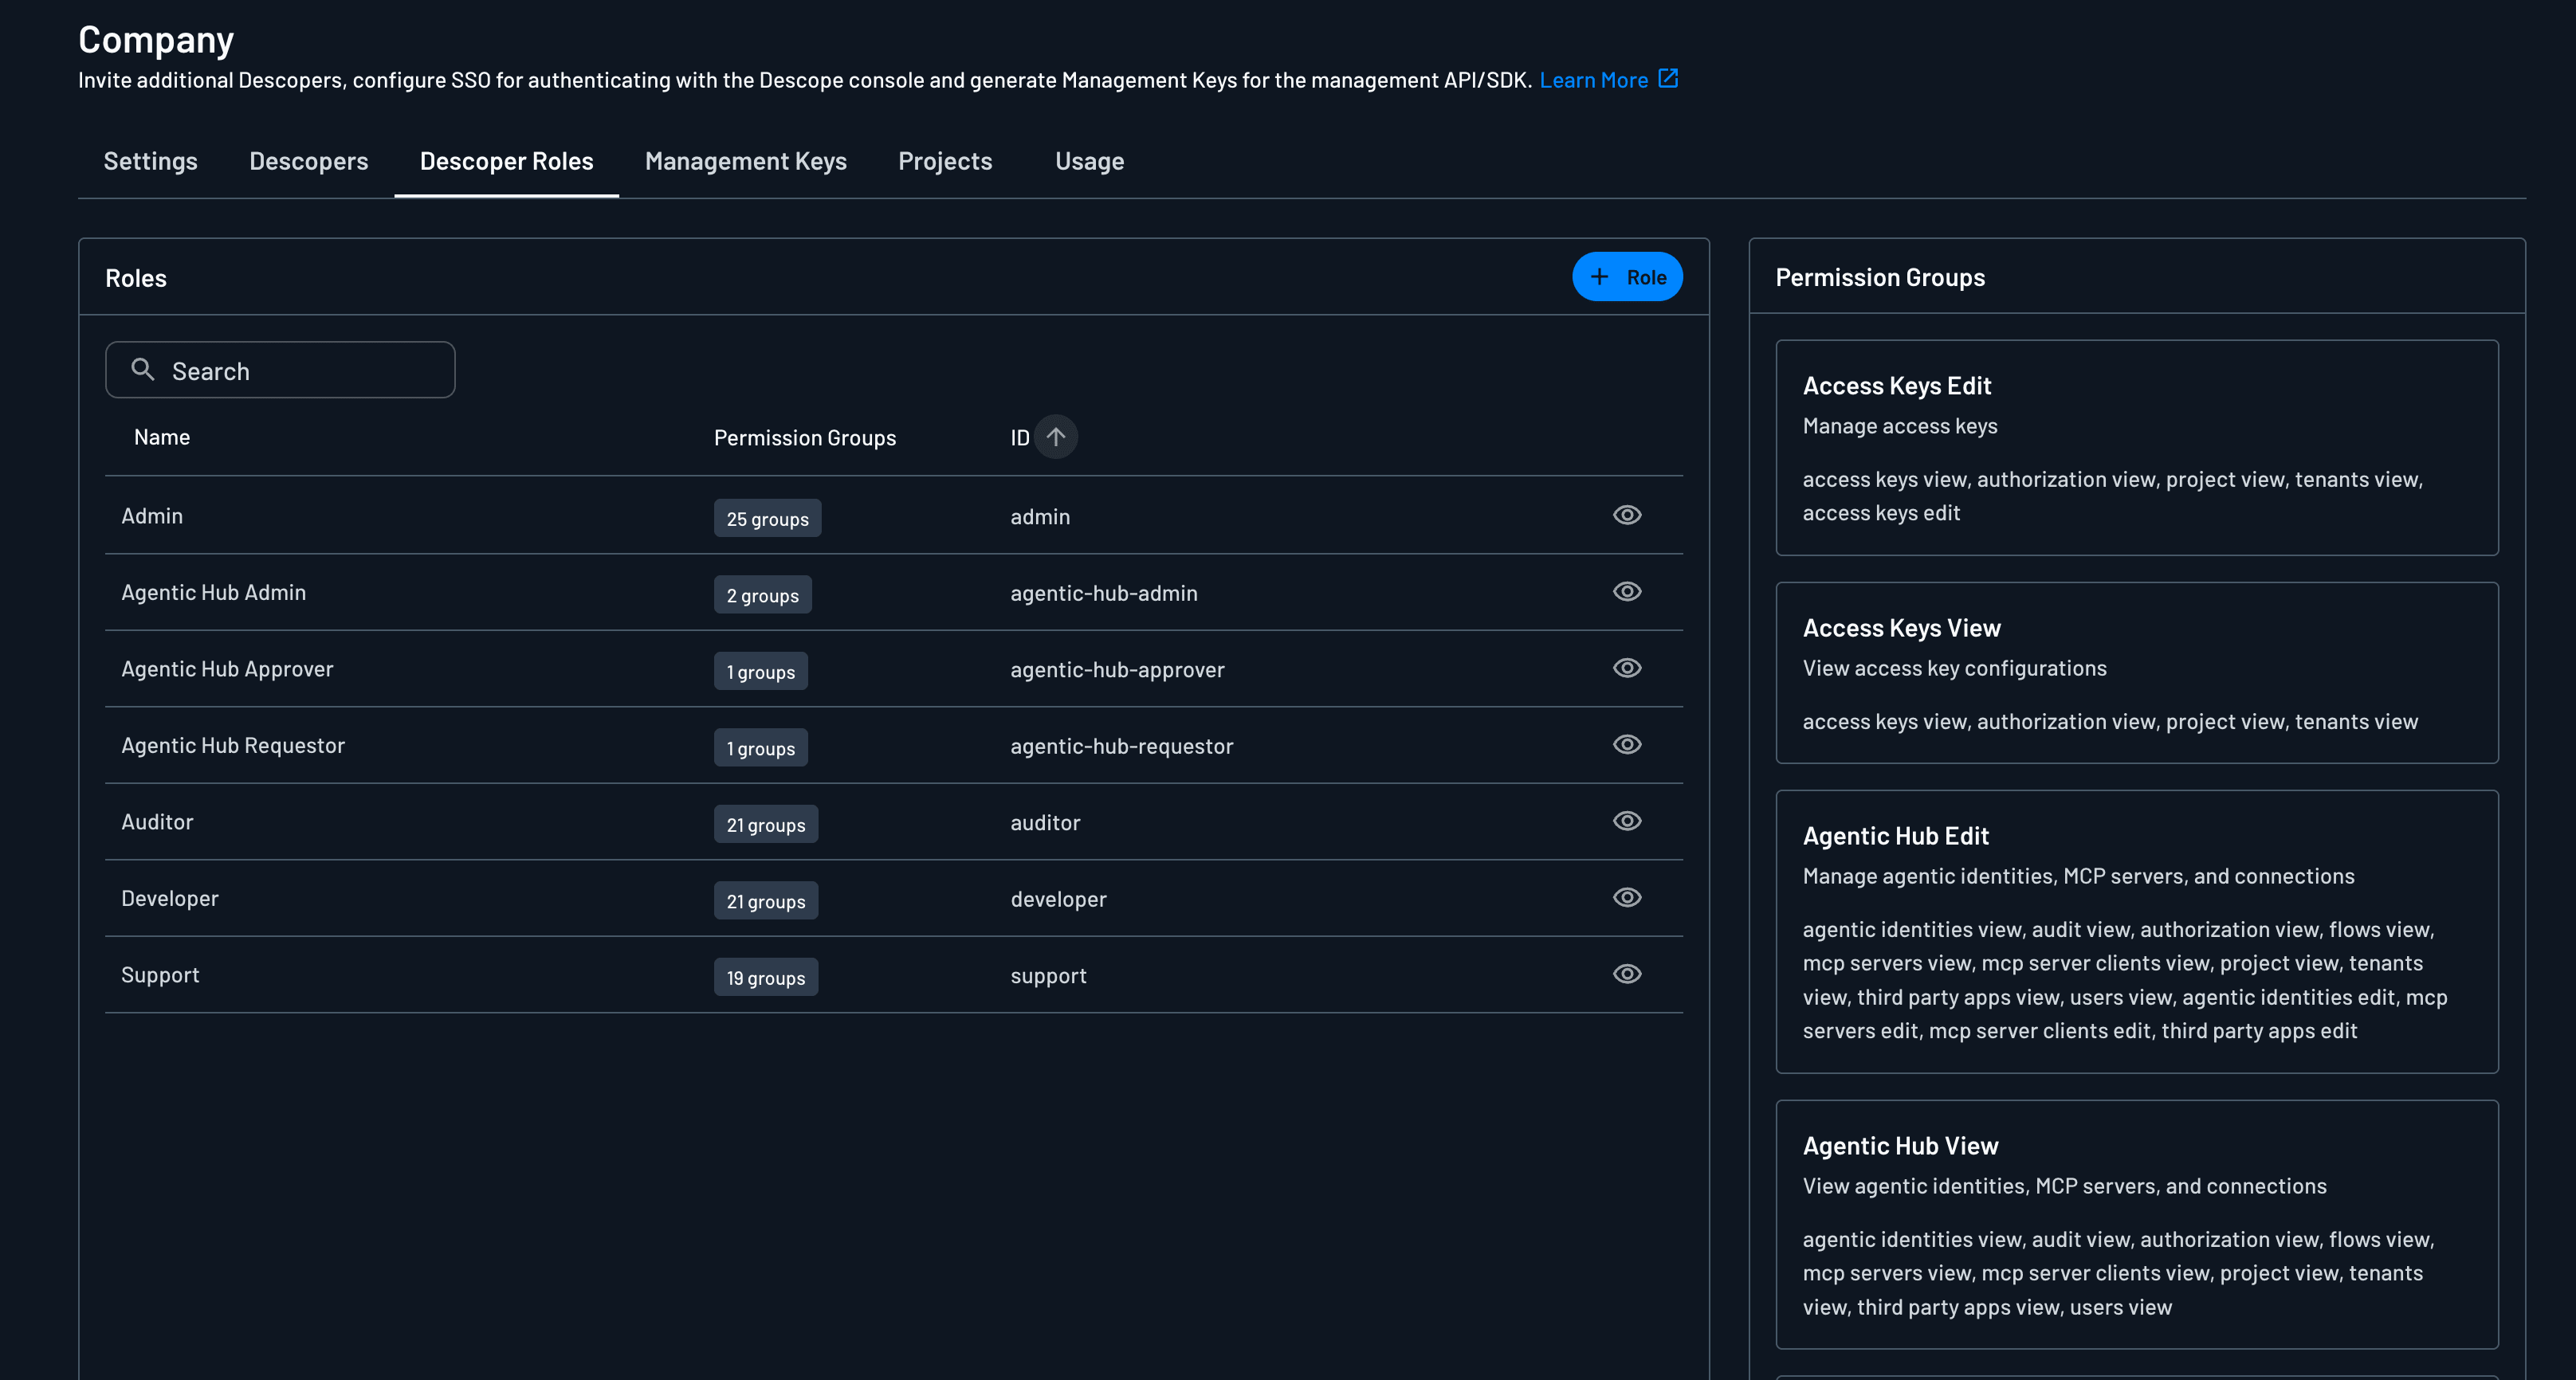
Descope includes the default roles below. Each role's access applies to the projects you assign it to on the Descopers tab.
| Role | Role ID | Access |
|---|---|---|
| Admin | admin | Full read and write access to the projects it's assigned to. |
| Developer | developer | Read and write access to the projects it's assigned to, including project settings. No access to company settings. |
| Support | support | Read access to Authentication Methods, Flows, Connectors, IdP Apps, Authorization, and Project Settings. Read and write access to users, access keys, tenants, and audit. |
| Auditor | auditor | |
| Agentic Hub Requestor | agentic-hub-requestor | Submits requests in the Agentic Governance Suite. Includes only the Agentic Hub Request permission group. |
| Agentic Hub Approver | agentic-hub-approver | Approves and denies Agent Governance requests. Includes the Agentic Hub Approve permission group. |
| Agentic Hub Admin | agentic-hub-admin | Approves requests and administers Agent Governance. Includes the Agentic Hub Approve and Agentic Hub Admin permission groups. |
To add a custom role, click + Role. Give the role a name and select one or more permission groups.
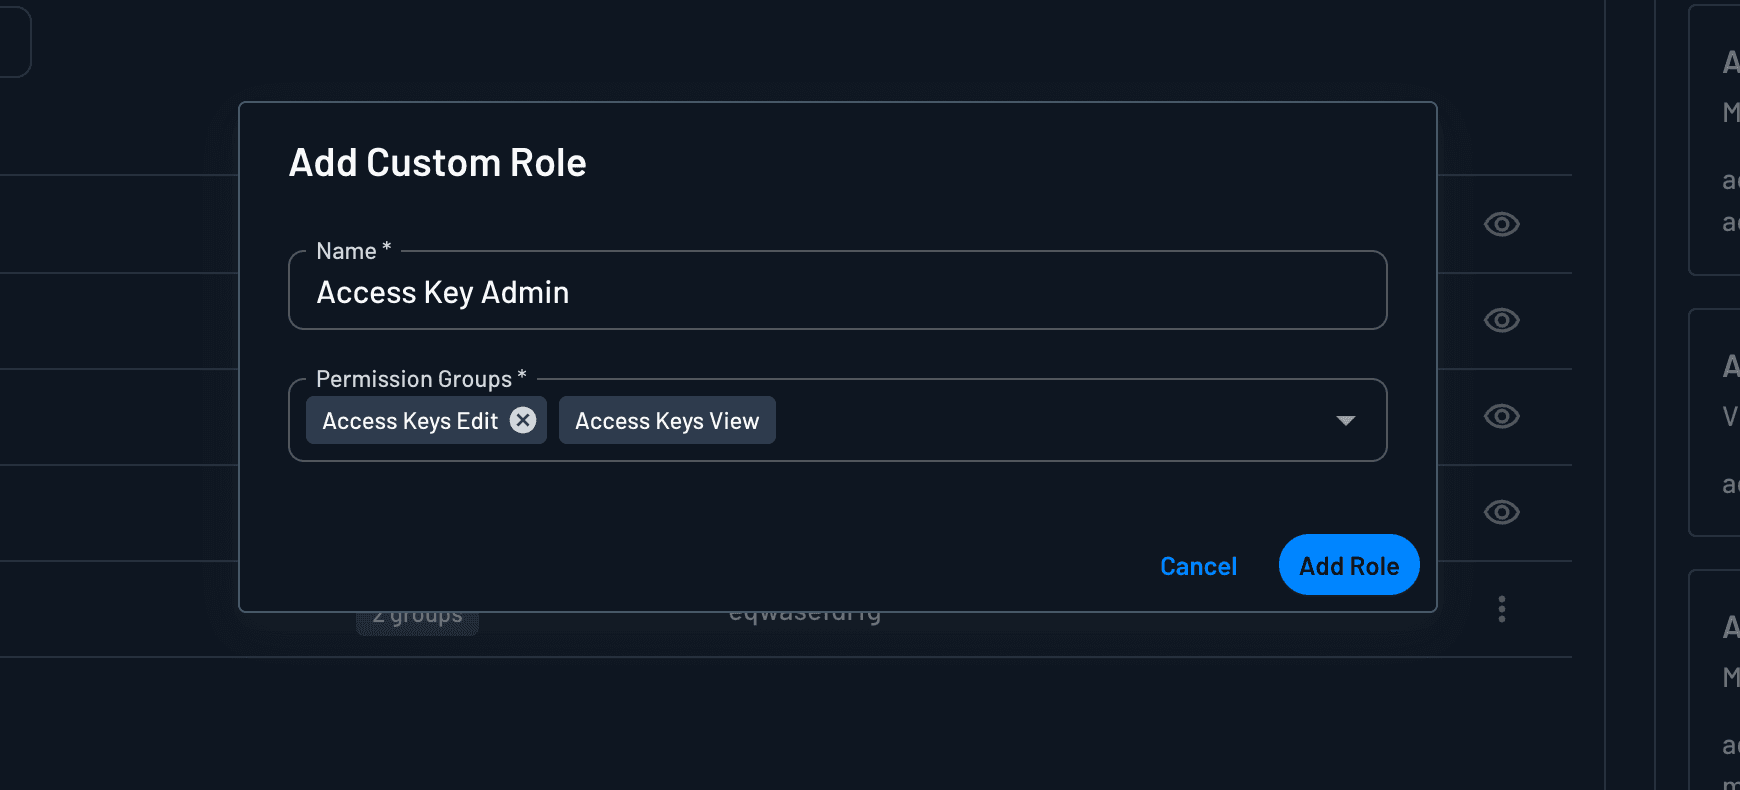
Permission Groups
The same tab lists every permission group. The permissions column lists the permissions inside each group.
| Permission group | Description | Permissions |
|---|---|---|
| Access Keys Edit | Manage access keys | access keys view, authorization view, project view, tenants view, access keys edit |
| Access Keys View | View access key configurations | access keys view, authorization view, project view, tenants view |
| Agentic Hub Admin | Administer Agent Governance, including its settings and portal | |
| Agentic Hub Approve | Approve, modify, and deny Agent Governance requests | |
| Agentic Hub Edit | Manage agentic identities, MCP servers, and connections | agentic identities view, audit view, authorization view, flows view, mcp servers view, mcp server clients view, project view, tenants view, third party apps view, users view, agentic identities edit, mcp servers edit, mcp server clients edit, third party apps edit |
| Agentic Hub Request | Submit and track Agent Governance requests in the portal | |
| Agentic Hub View | View agentic identities, MCP servers, and connections | agentic identities view, audit view, authorization view, flows view, mcp servers view, mcp server clients view, project view, tenants view, third party apps view, users view |
| Audits View | View audit logs and activity history | audit view, tenants view |
| User Access Policy Edit | Manage the authentication access policy | auth access view, project view, auth access edit |
| User Access Policy View | View the authentication access policy | auth access view, project view |
| Authentication Methods Edit | Configure authentication methods | auth methods view, authorization view, project view, users view, tenants view, styles view, audit view, connectors view, flows view, auth methods edit, connectors edit |
| Authentication Methods View | View authentication method configurations | auth methods view, authorization view, project view, users view, tenants view, styles view, audit view, connectors view, flows view |
| Authorization Edit | Manage roles, permissions, and FGA configuration | authorization view, auth roles edit, auth permissions edit |
| Authorization View | View roles, permissions, and FGA configuration | authorization view |
| Connectors Edit | Configure and manage connectors | audit view, auth methods view, connectors view, flows view, tenants view, project view, connectors edit |
| Connectors View | View connector configurations | audit view, auth methods view, connectors view, flows view, tenants view, project view |
| Families Edit | Manage families and their settings | families view, project view, users view, families edit |
| Families View | View family configurations | families view, project view, users view |
| Flows Edit | Create and modify authentication flows | flows view, auth methods view, connectors view, project view, users view, authorization view, sso apps view, styles view, tenants view, flows edit |
| Flows View | View authentication and authorization flows | flows view, auth methods view, connectors view, project view, users view, authorization view, sso apps view, styles view, tenants view |
| Getting Started | Run the "Getting Started" setup wizard | home trigger wizard, wizard view, wizard edit, flows view, flows edit, project view, tenants view, styles view, styles edit |
| Home View | View the project home dashboard and overview | home view, audit view, connectors view, flows view, project view, tenants view, third party apps view |
| Inbound Apps Edit | Configure inbound applications | third party apps view, authorization view, flows view, project view, users view, tenants view, third party apps edit |
| Inbound Apps View | View inbound application configurations | third party apps view, authorization view, flows view, project view, users view, tenants view |
| Localization Edit | Manage localization and translations | auth methods view, connectors view, flows view, third party apps view, auth methods edit, flows edit, third party apps edit |
| Localization View | View localization and translations | auth methods view, connectors view, flows view, third party apps view |
| Outbound Apps Edit | Configure outbound applications | sso apps view, third party apps view, tenants view, sso apps edit, third party apps edit |
| Outbound Apps View | View outbound application configurations | sso apps view, third party apps view, tenants view |
| Project Settings Edit | Manage project settings | project view, tenants view, auth methods view, connectors view, audit view, flows view, users view, project edit, connectors edit |
| Project Settings View | View project settings and configuration | project view, tenants view, auth methods view, connectors view, audit view, flows view, users view |
| Federated Applications Edit | Configure federated applications | audit view, authorization view, flows view, sso apps view, users view, auth methods view, sso apps edit |
| Federated Applications View | View federated application configurations | audit view, authorization view, flows view, sso apps view, users view, auth methods view |
| Style Editor Edit | Customize flow styles and branding | styles view, auth methods view, styles edit |
| Style Editor View | View flow styles and branding | styles view, auth methods view |
| Tenants Edit | Manage tenants and their settings | auth methods view, authorization view, connectors view, project view, sso apps view, tenants view, users view, styles view, tenants edit |
| Tenants View | View tenant configurations | auth methods view, authorization view, connectors view, project view, sso apps view, tenants view, users view, styles view |
| Users & Custom Attributes Edit | Manage user accounts, including custom attributes | authorization view, project view, sso apps view, tenants view, users view, connectors view, users edit, users ca edit |
| Users Edit | Manage user accounts. This group does not include custom attribute editing | authorization view, project view, sso apps view, tenants view, users view, connectors view, users edit |
| Users View | View user accounts and details | authorization view, project view, sso apps view, tenants view, users view, connectors view |
| Widgets Edit | Configure and customize widgets | styles view, auth methods view, connectors view, project view, users view, tenants view, flows view, authorization view, sso apps view, styles edit, flows edit |
| Widgets View | View widget configurations | styles view, auth methods view, connectors view, project view, users view, tenants view, flows view, authorization view, sso apps view |
Management Keys
Within the Management Keys tab you can create, delete, and manage Management keys within your company.
Review the Management Keys documentation for more information about how they can be used.
Projects
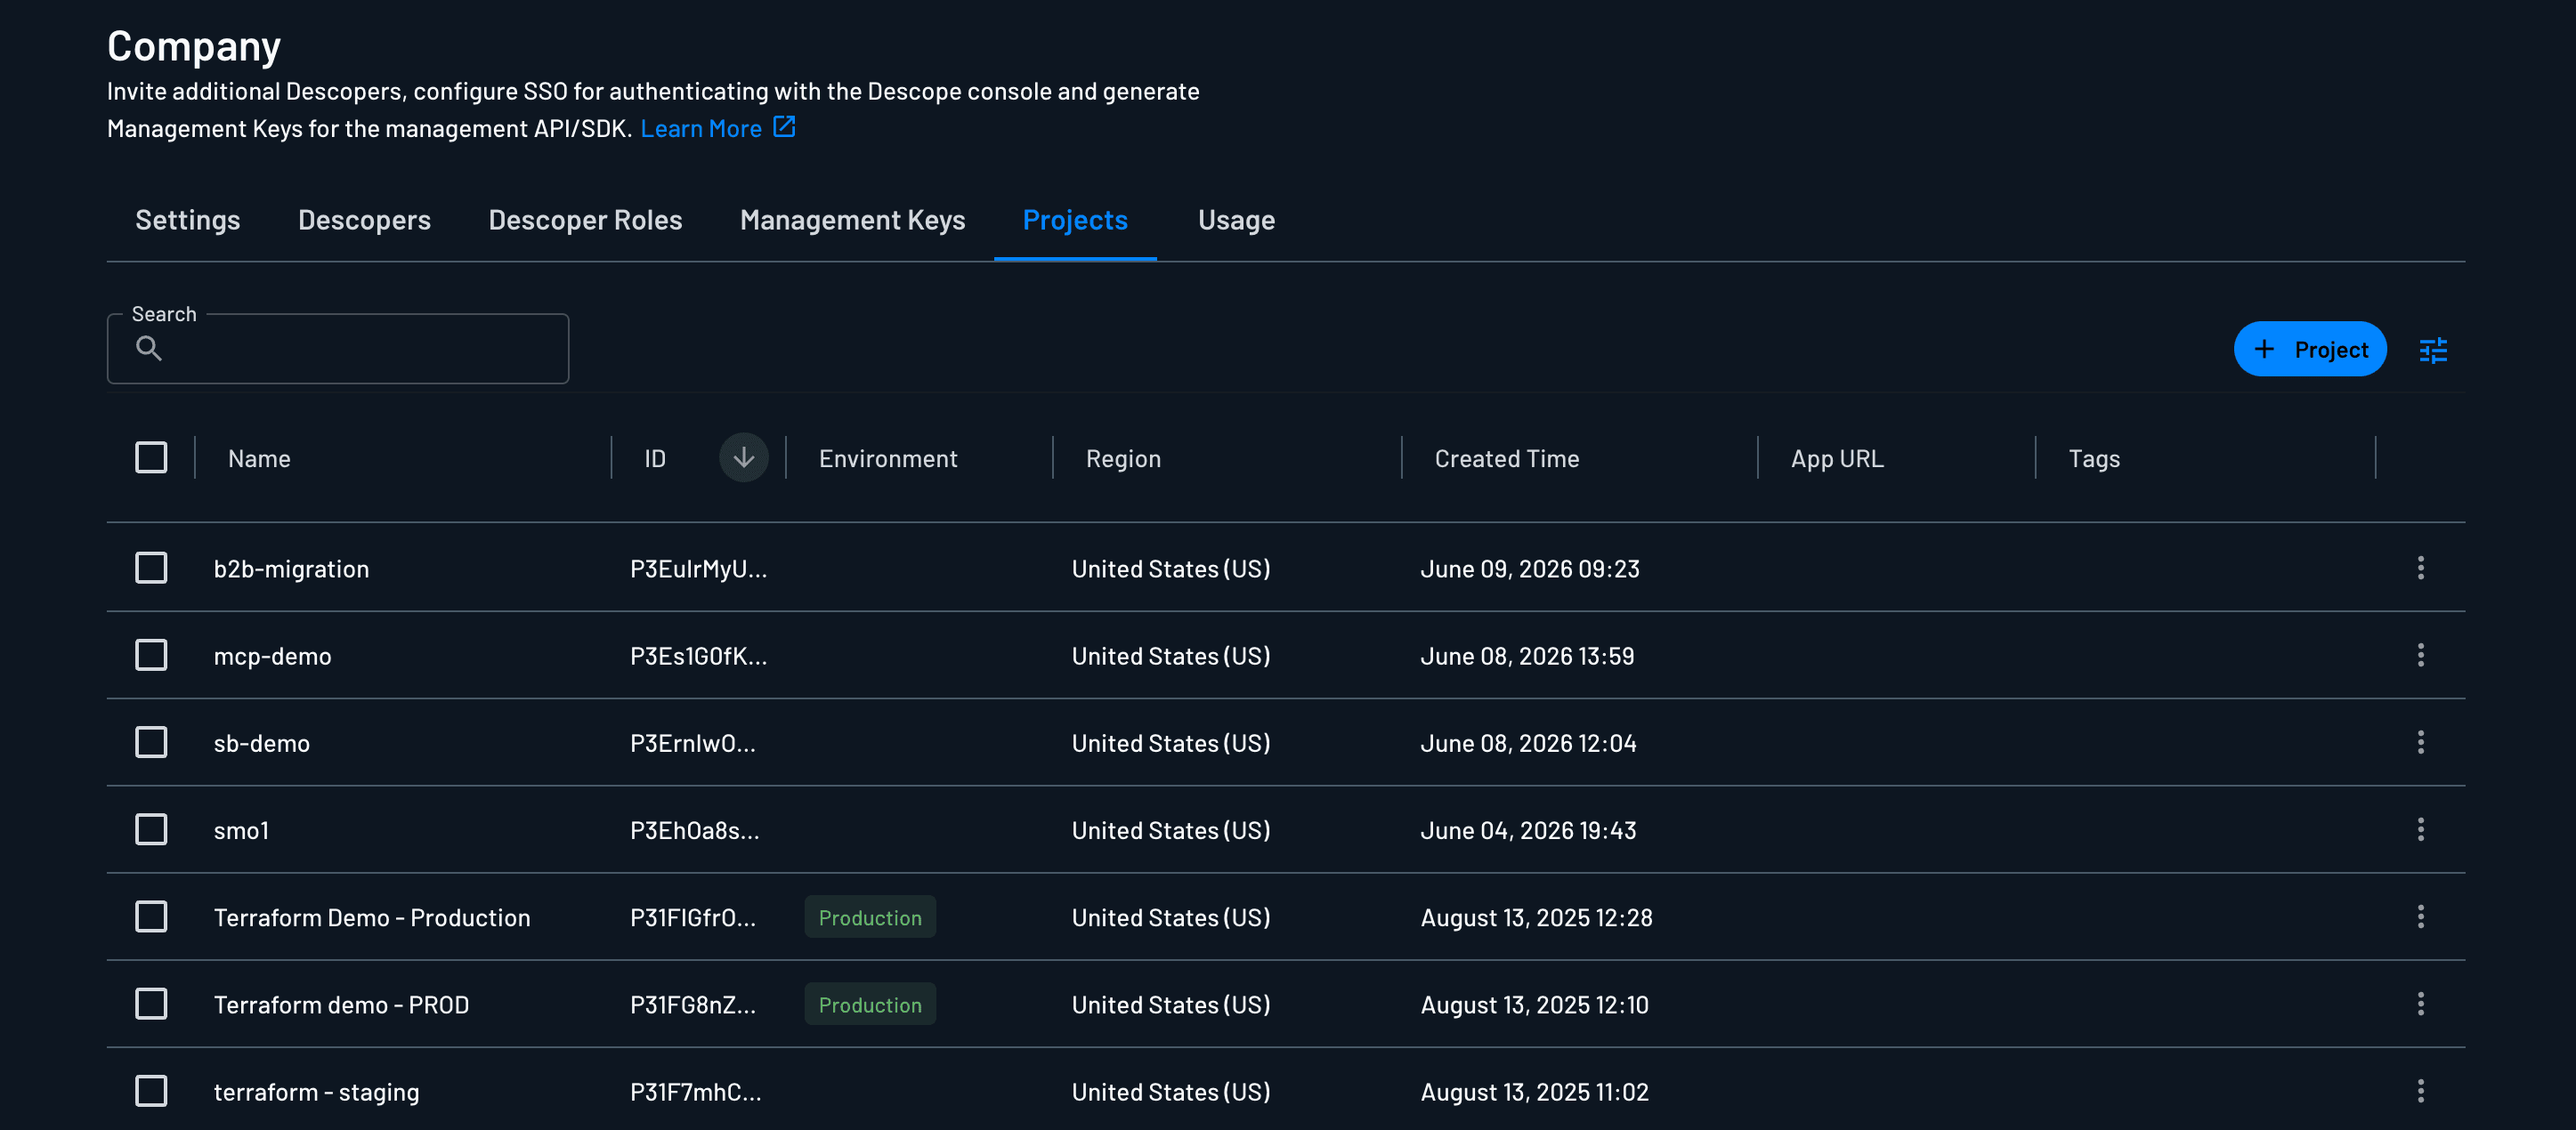
On the Projects tab you see every project in your company. Selecting a project opens its project page so you can edit that project's settings. The settings icon at the end of each row opens more actions: Edit, Clone, Export (Pro plan only), and Delete.
The projects table includes the following columns. Click the arrow next to any column header to sort in ascending or descending order. Optional columns can be shown or hidden from the column picker.
| Column | Description |
|---|---|
| Name | The display name of the project. |
| ID | The unique project identifier. |
| Environment | The project environment (for example, development, staging, or production). |
| Region | The geographic region where the project is deployed. |
| Created Time | When the project was created. |
| App URL | The application URL which your application resides on. |
| Tags | Custom labels used to organize and filter projects. |
| Block Sign Up Config | Whether sign-up is blocked for the project. (Optional column) |
| Custom Domain | The custom domain configured for the project. (Optional column) |
| Approved Domain | Domains allowed for redirect and verification URLs across authentication methods. (Optional column) |
Use the search filter to narrow the project list by different fields when you have many projects. To create a new project, click the +Project button on the right.
Usage
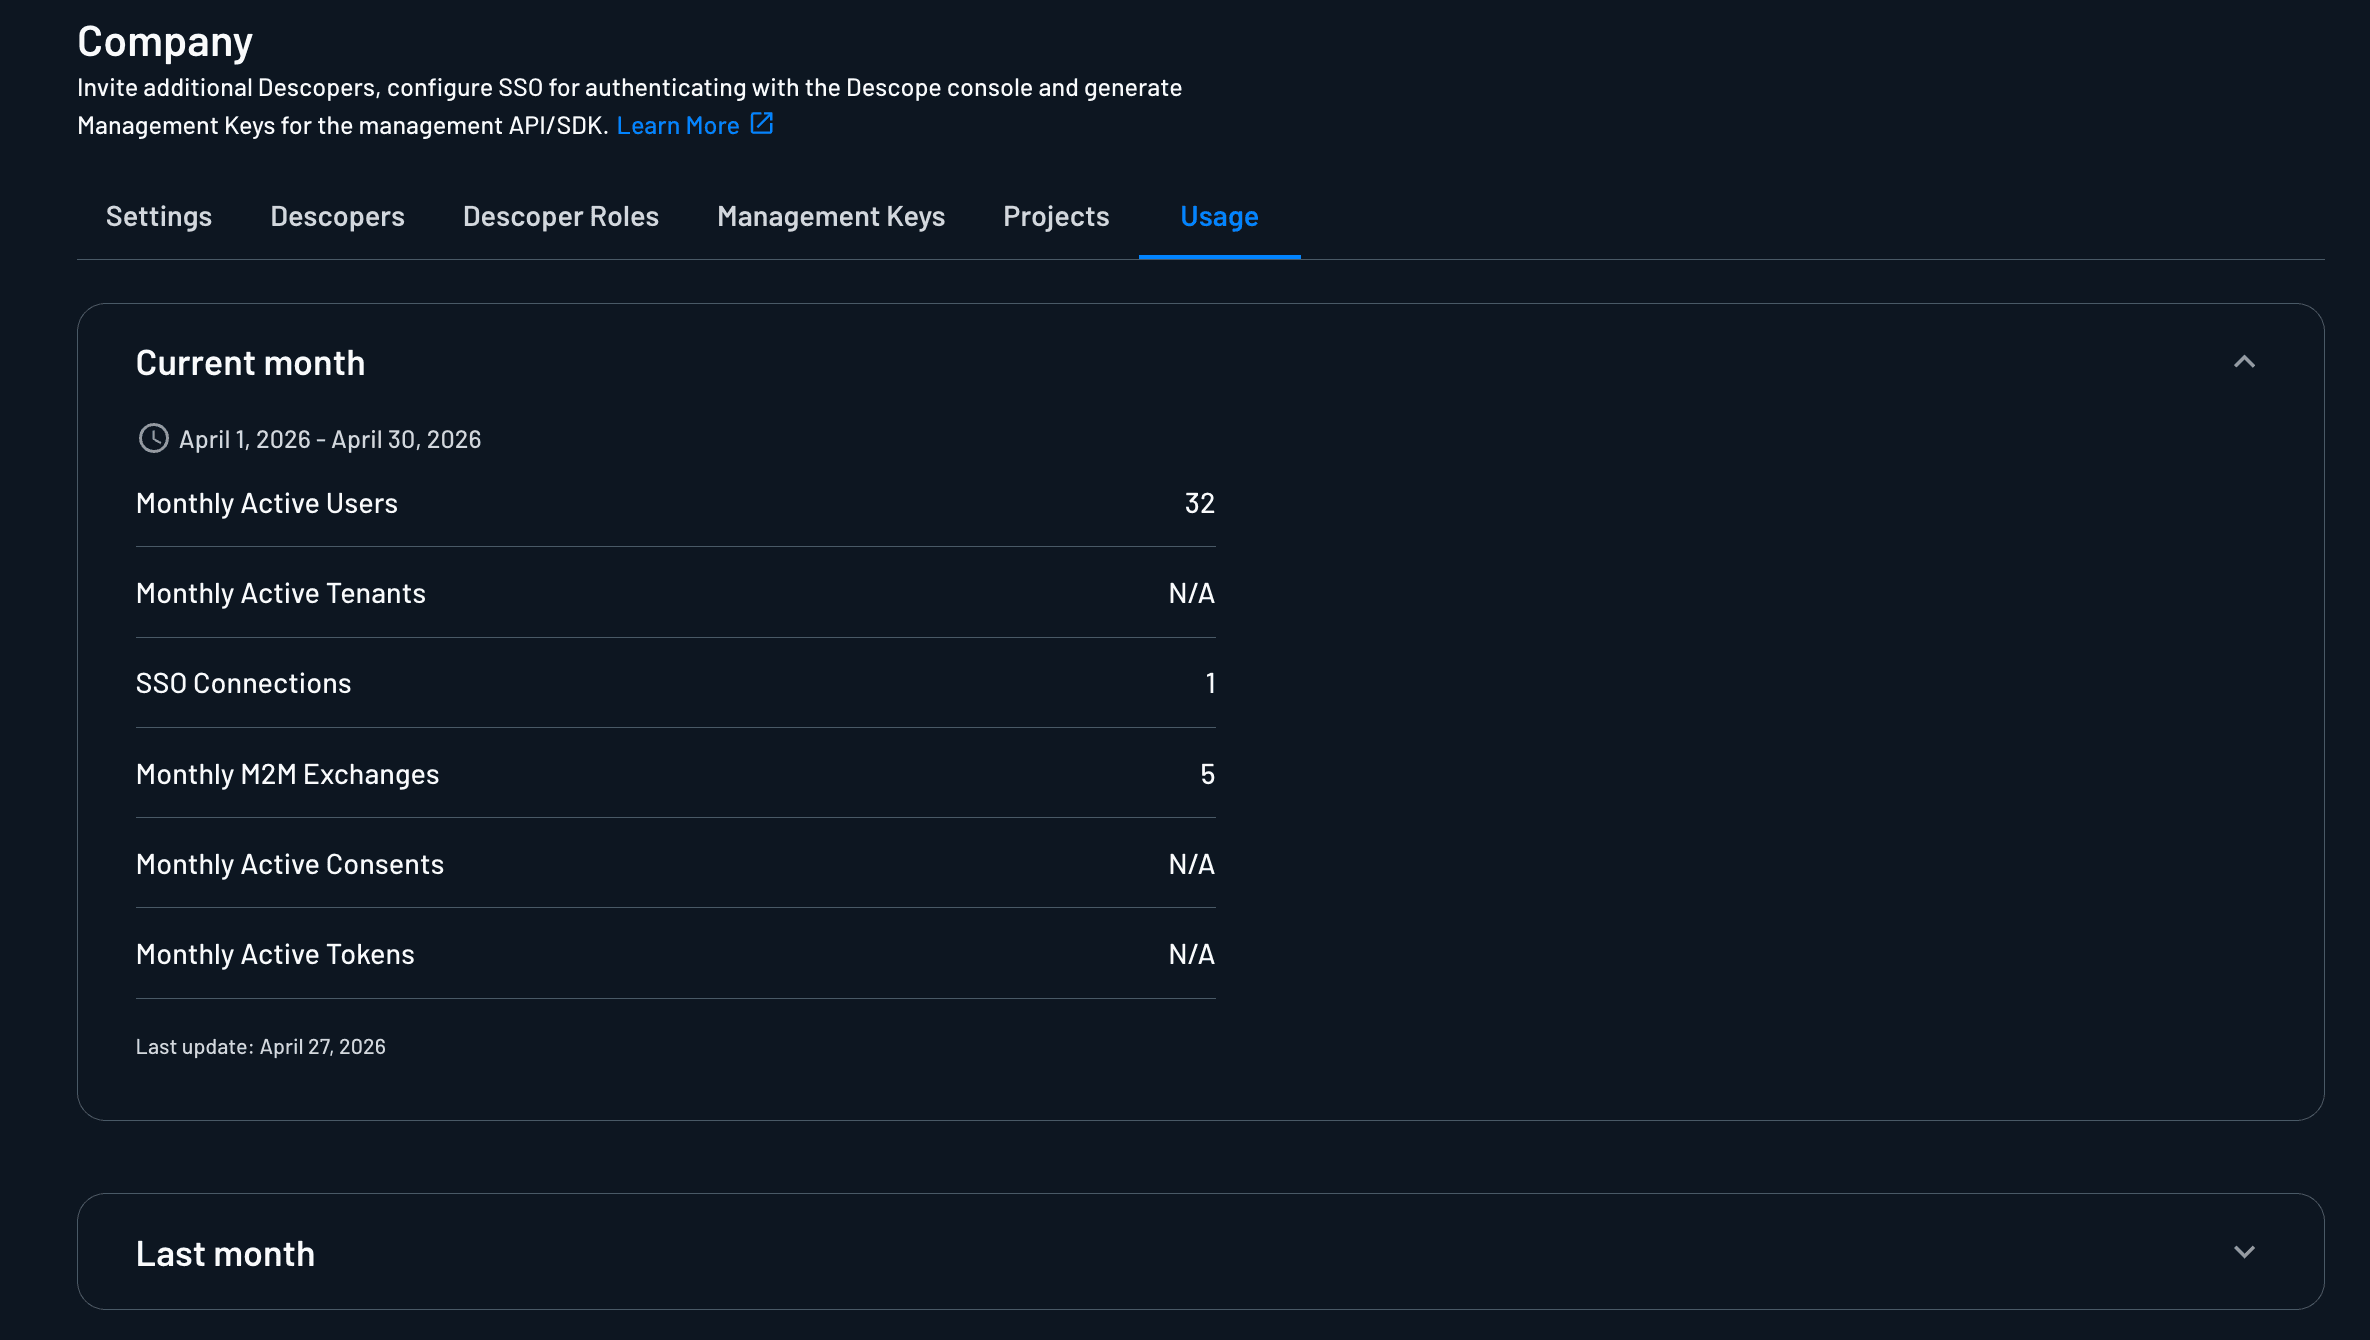
The Usage tab on Company Settings summarizes usage metrics for your company. For each metric you can see totals for the current month and the previous month:
- Monthly Active Users
- Monthly Active Tenants
- SSO Connections
- Monthly M2M Exchanges
- Monthly Active Consents
- Monthly Active Tokens
For plan allowances, how overages work, and explanations of this terminology, see Descope pricing.
Note
For a detailed breakdown of your M2M usage, contact Descope Support to request a usage report.